Home Blog

Understanding Automotive Technology Platforms: Techcarz Com

0

The Convergence of Automotive Engineering and Digital Software

There was a time when evaluating a new car meant talking about cylinder displacement, horsepower curves, mechanical differential locks, and the tactile click of a short-throw gear lever. While fundamental physics still dictates how a vehicle handles a tight corner, physical hardware no longer acts as the sole defining feature of modern transport. Over the past decade, the automotive sector has undergone an unprecedented migration toward software-defined vehicles (SDVs), centralized high-performance computing, integrated electric powertrains, and cloud-connected cockpit architectures.

Today, a modern automobile behaves much like a sophisticated mobile edge computing node on wheels. Millions of lines of code govern everything from battery thermal conditioning to active lane centering and regenerative braking curves. As vehicles become increasingly reliant on silicon and software stack updates, the nature of automotive journalism and technical reporting has evolved alongside them. Outlets like techcarz com have emerged to bridge the gap between traditional motoring reviews and deep-tech analysis, helping everyday drivers, engineers, and tech enthusiasts make sense of how microprocessors, sensor arrays, and wireless protocols alter daily driving mechanics, long-term reliability, and ownership costs.

For motorists across India and globally, staying informed about over-the-air firmware upgrades, state-of-charge algorithms, and embedded telematics isn’t just an academic exercise—it directly impacts vehicle safety, resale value, and functional utility. Understanding how modern technology portals dissect these systems provides essential context for navigating an increasingly complex, digitally driven automotive marketplace.

Why Portals Like techcarz com Are Essential for Modern Car Owners
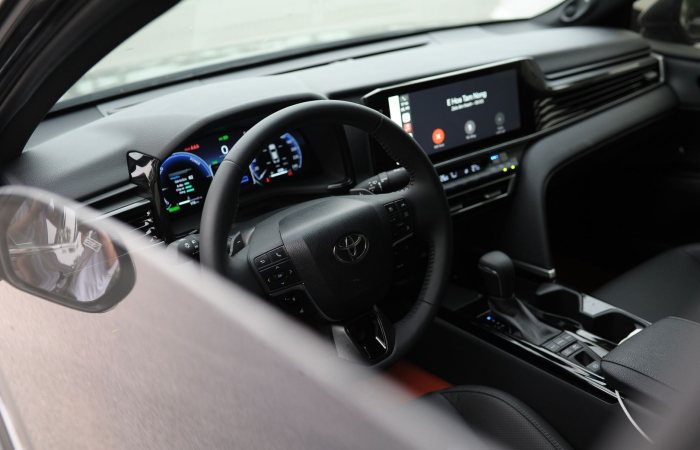
High-tech interior of a modern car featuring dashboard and digital display.

As vehicle electronics grow exponentially more intricate, consumer education becomes a vital line of defense against marketing hyperbole. The average buyer shopping for an electric or connected vehicle is confronted with a barrage of technical jargon: CAN bus architecture, silicon carbide (SiC) inverters, lithium iron phosphate (LFP) vs. nickel manganese cobalt (NMC) chemistries, level 2+ autonomy, and OTA telemetry pipelines. Specialized media platforms translate these dense engineering principles into clear, practical consumer insights.

When readers explore deep-dive analysis on techcarz com, they encounter content structured around four fundamental pillars that define modern automotive technology:

  • In-Vehicle Infotainment (IVI) & Cockpit UX: Evaluating native operating systems like Android Automotive OS, wireless smartphone integration protocols, digital cluster responsiveness, head-up displays (HUD), and intuitive natural language voice control interfaces.
  • Electric Mobility & Powertrain Management: Unpacking 400V vs. 800V charging architectures, regenerative braking calibration, inverter efficiency gains, thermal management during rapid DC charging, and real-world battery health monitoring.
  • Connected Telematics & V2X Infrastructure: Assessing embedded eSIM connectivity, remote vehicle monitoring applications, fleet tracking software, and nascent vehicle-to-everything (V2X) communications that allow cars to signal traffic infrastructure and surrounding traffic.
  • Automotive Cybersecurity & Hardware Resilience: Tracking end-to-end data encryption, Hardware Security Modules (HSMs), network isolation between non-critical infotainment and critical drive controllers, and compliance with emerging international cybersecurity regulations.

A closer look at published insights on techcarz com reveals a rapid acceleration in consumer interest, particularly within emerging markets like India. Drivers are no longer content simply knowing a car’s zero-to-sixty acceleration; they want to know how quickly the onboard systems boot up, how frequently the manufacturer pushes firmware patches, and whether their personal telemetry data remains private.

Key Pillars of Modern Connected Vehicles
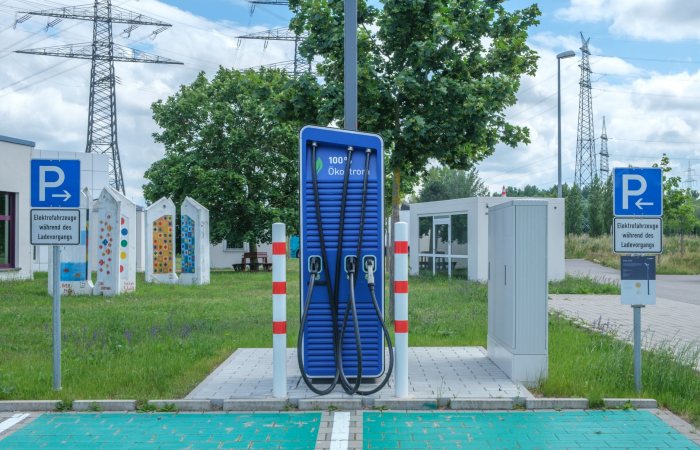
Public charging station with eco-friendly design for electric vehicles.

To fully grasp the discussions taking place across technical automotive forums, one must understand the core architectural shifts underway inside modern vehicle platforms. These foundational shifts dictate how cars are engineered from the ground up, how they interact with their environments, and how they improve—or degrade—over time.

1. Domain and Zonal Controller Architectures

For decades, vehicles relied on decentralized networks made up of dozens—sometimes over a hundred—isolated Electronic Control Units (ECUs). Each ECU handled a single discrete task: one controlled the power windows, another managed the anti-lock braking system, and a third operated the climate control panel. This setup required miles of heavy, costly copper wiring harnesses and made system-wide communication agonizingly slow.

Modern software-defined vehicles abandon this fragmented approach in favor of domain and zonal control architectures. High-performance central compute units consolidate multiple functions into unified software domains running on real-time operating systems (RTOS). This shift drastically reduces wiring complexity, sheds physical weight, and enables manufacturers to update vehicle behavior—from throttle mapping to suspension dampening—through centralized software patches delivered over the air.

2. Cloud Telematics and Predictive Diagnostics

Connected vehicles continuously stream operational telemetry to secured cloud servers. This data stream creates a continuous feedback loop between the vehicle and the engineering team. Rather than waiting for a mechanical component to fail or relying entirely on fixed mileage service schedules, cloud telemetry enables predictive maintenance routines.

Algorithms analyze micro-variations in electrical resistance, battery cell voltage divergence, pump pressures, and vibration profiles to identify failing hardware long before a warning light illuminates on the dashboard. Fleet operations leverage these diagnostics to minimize vehicle downtime, while individual owners benefit from proactive service alerts sent straight to their smartphones.

3. Advanced Driver Assistance Systems (ADAS) and Sensor Fusion

Modern driver assistance features rely on sensor fusion—the mathematical integration of data captured simultaneously by optical cameras, radar units, ultrasonic transducers, and, in high-end applications, LiDAR. Sensor fusion algorithms cross-reference input feeds to generate a dynamic 360-degree digital map of the environment surrounding the vehicle.

This contextual awareness enables critical safety features like automatic emergency braking, adaptive cruise control with stop-and-go functionality, blind-spot collision avoidance, and automated lane changing. However, objective technical writing emphasizes that these systems remain driver-assist tools rather than fully autonomous pilots; clear public education is necessary to ensure drivers understand system boundaries and remain engaged behind the wheel.

Comparing Traditional Mechanical Vehicles and Software-Defined Vehicles
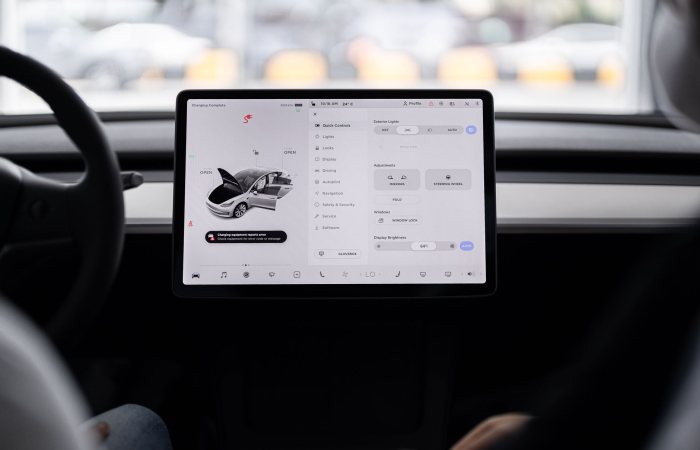
View of a modern car's dashboard featuring a digital display panel with control options.

The transition from hardware-first vehicle engineering to software-centric platforms fundamental changes how cars are built, serviced, monetized, and resold. The table below outlines the core practical distinctions between these two automotive paradigms.

Feature Attribute Traditional Mechanical Vehicles Software-Defined Vehicles (SDVs)
Feature Lifecycle Static upon factory departure; capabilities remain fixed throughout service life. Dynamic; continuous expansion via over-the-air (OTA) software updates.
Maintenance Model Reactive; scheduled mechanical inspections or response to component breakdown. Predictive; continuous cloud telemetry monitoring real-time component health.
Security Architecture Physical key tumblers, steering locks, and basic engine immobilizer chips. Hardware Security Modules (HSMs), encrypted CAN bus traffic, and cloud firewalls.
Depreciation Dynamics Monotonic value decline driven primarily by age, mileage, and mechanical wear. Non-linear retention; feature updates and range optimizations can stabilize market value.
Data & Privacy Footprint Minimal data footprint; localized error codes readable via diagnostic ports. Extensive data generation; location logs, driver metrics, and user preferences stored on clouds.

Evaluating Automotive Content: A Reader’s Framework

With an endless stream of automotive news aggregators, press release republishers, and commercial blogs crowding search engine results, discerning readers need a structured framework to evaluate technical claims. When reading detailed industry breakdowns on techcarz com or examining manufacturer whitepapers independently, applying a critical eye protects consumers from marketing fluff and unverified performance claims.

Critical Evaluation Checklist

  1. Distinguish Theoretical Specs from Real-World Testing: EPA, WLTP, or ARAI range figures are calculated under controlled laboratory conditions. Real-world electric vehicle range is severely impacted by ambient temperature, cabin climate control usage, aerodynamic drag at highway speeds, elevation changes, and tire selection. Look for analysis grounded in real-world road tests.
  2. Verify Hardware and Software Prerequisites: Software updates and app integration guidelines often contain regional or hardware-specific caveats. Ensure technical guides clearly differentiate between vehicle model years, trim levels, chipsets, and operating system builds before attempting troubleshooting or purchasing feature unlocks.
  3. Scrutatize Privacy Practices and Monetization Models: As cars become rolling consumer data hubs, research how manufacturers process personal metrics. Reputable publications highlight whether driver data—such as speed logs, hard braking events, and location histories—is sold to third-party insurance brokers or securely anonymized.
  4. Assess Long-Term Software Support Windows: A vehicle outlives the typical software lifecycle of a smartphone or tablet. Evaluate whether legacy hardware platforms will continue receiving security patches, map updates, and app support five to ten years down the road.

Data Privacy and Security Considerations in Smart Mobility

As vehicles integrate deeper into the Internet of Things (IoT) ecosystem, their attack surface expands dramatically. A modern connected vehicle communicates continuously over cellular networks, Bluetooth, Wi-Fi, and GPS signals. Without rigorous defensive security, vulnerabilities in third-party mobile applications, infotainment web browsers, or remote telemetry gateways could give malicious actors unauthorized access to location history, cabin microphones, or vehicle controls.

To counter these risks, automotive regulatory bodies have introduced strict standards, such as UN Regulation No. 155 (UN R155) and ISO/SAE 21434. These guidelines mandate structured Cybersecurity Management Systems (CSMS) across the entire vehicle design, supply chain, and operational lifecycle.

Key defensive safeguards include:

  • Network Micro-segmentation: Isolating non-essential user domain networks (like cabin Wi-Fi and infotainment) from safety-critical powertrain, steering, and braking controller networks using secure gateway firewalls.
  • Cryptographic Code Signing: Requiring explicit cryptographic digital signatures on all incoming over-the-air firmware binaries to ensure the vehicle only executes authentic, un-tampered manufacturer code.
  • Secure Hardware Modules: Utilizing dedicated physical silicon chips (Hardware Security Modules) inside onboard domain controllers to securely store cryptographic keys, passwords, and sensitive user identification credentials.

When reading security coverage on techcarz com, prioritizing platforms that address cybersecurity threats with objective clarity helps drivers understand their rights, adjust app permission settings appropriately, and demand better privacy practices from original equipment manufacturers (OEMs).

Frequently Asked Questions

What core topics does an automotive technology platform cover?

An automotive technology platform focuses on the intersection of transport engineering and computer science. Coverage typically spans electric vehicle battery architectures, software-defined vehicle designs, autonomous driving sensor suites, in-vehicle infotainment ecosystems, connected fleet telematics, and automotive cybersecurity frameworks.

How do over-the-air (OTA) updates work in modern vehicles?

Over-the-air updates deliver software patches, map updates, and system tweaks directly to a car’s onboard cellular module. Once downloaded, the system verifies the update’s digital signature for security. The driver is then prompted to install the update while the vehicle is safely parked, updating onboard domain controllers without requiring a physical service appointment.

Where can motorists find reliable analysis like that on techcarz com?

Detailed analysis of the type found on techcarz com can be accessed directly through specialized online automotive technology journals, dedicated EV research portals, and engineering publications that focus on real-world vehicle software testing, telematics evaluations, and independent range benchmarks.

Why is thermal management critical for electric vehicle performance?

Lithium-ion batteries operate within a narrow optimal temperature window. Thermal management systems use liquid coolant loops, heat pumps, and resistive heaters to keep battery packs cool during fast DC charging and warm during freezing weather. Proper thermal management preserves fast-charging speeds, maintains consistent power delivery, and prevents long-term capacity degradation.

Conclusion

The line dividing automotive engineering from software development has permanently blurred. Cars are no longer static mechanical machines that remain unchanged from the moment they roll off the assembly line; they are dynamic, cloud-connected digital platforms that continuously adapt, update, and generate data throughout their operational life.

Navigating this complex ecosystem requires clear, objective, and technically grounded reporting. Independent media channels like techcarz com play a vital role in demystifying complex concepts—ranging from domain controller consolidation and OTA firmware updates to battery chemistry dynamics and cybersecurity regulations. By focusing on technical reality rather than market hype, motorists and tech enthusiasts alike can evaluate new mobility trends with clarity, make informed purchasing choices, and safely embrace the future of connected transport.

Related Guides

Explore more useful resources related to this topic:
About the Author

Shaista Rafi — Business Development Team Lead

Shaista Rafi works on SEO-focused content systems, website growth and digital publishing workflows.

10 Benefits of Demand Side Platforms

0

Today’s market is complex, which means you need to be at the top-notch of your game with your marketing and advertising campaigns. A demand side platform (DSP) is designed to help advertisers manage their campaigns. By controlling a DSP, you can delegate your campaign to a specialist who will work tirelessly to ensure the best performance possible.

A DSP makes the job of the advertisers, agencies, and ad networks easier. By taking control of your campaign with a DSP, you will realize its significant benefits.

Here are ten reasons why DSP is becoming so important in today’s market.

Targeted Traffic

In B2B advertising, you should strive to obtain high-quality daily targeted traffic by using demand-side platforms. If you aren’t familiar with what DSPs are, don’t worry about it right now. Just think of them as places where your advertisements get displayed to consumers instead of publishers.

Sales Volume

The key to success in ad technology is getting your advertisement in front of as many eyes as possible. A demand-side platform aims to help marketers reach that audience by promising them access to real-time bid requests. This means that a demand side platform offers a large daily volume of bid requests from programmatic buyers and guaranteed ad placement if you’re willing to pay for it.

Daily ROI

Using a DSP, you’ll be able to gauge and improve your return on investment daily. For example, you can see if your ads are profitable and also track CPA and ROAS performance. Using DSPs enables you to analyze campaign data in real-time, so you can instantly change or remove unprofitable bids! By identifying poor-performing creatives before they even go live, DSPs can also prevent wasted ad spending.

Daily Leads

Today’s advertising market is all about measurable results. Advertisers are looking for ways to understand if they are effectively spending their money, and DSPs make it easier than ever to reach that by using technology to identify customers who are ready to buy right now. Plus, advertisers love programmatic buying because it allows them to adjust campaigns quickly in response to changing trends or even just popular demands from clients.

Brand Visibility

Nearly every major retailer on both sides of the pond uses DSPs to buy advertising space. It’s becoming increasingly important for media buyers and everyday consumers looking to cut through all that clutter with their wallets. The power lies in visibility! DSPs offer an unprecedented level of transparency into how inventory is priced and how many impressions are available at any given time.

Revenue Optimization

DSPs optimize auctions and focus on the most relevant audiences to increase daily revenue. A DSP can quickly change bids in response to numerous factors, including geographic location, customer profile, time, and more. That data will inform your budget allocations to maximize return-on-investment for your campaigns.

Product Feed Management

Even if you have an in-house team to update product feeds, managing products at scale takes time. In addition, there is a risk of having employees who aren’t experts in updating inventory and prices. With a demand-side platform, you can rely on data from your clients to update product feeds without human intervention or fallibility.

Inventory Updates

A DSP offers real-time bidding (RTB) and delivers new inventory data on an hourly basis. What does that mean for you? By using real-time bidding, you know your bids are as optimized as possible and maximized to their full potential. However, it is nearly impossible to adjust once they have been sent, which is why having new inventory data every hour allows you to track results more closely.

Reporting Completed Requests

If you use DSPs to manage your ad inventory, they’ll provide you with daily reporting. This is a handy feature of an ad platform because it gives you detailed information about which ads are performing best at what times to optimize future campaigns accordingly. A daily snapshot of how your ads are performing is invaluable when working to increase ROI.

Account Executive Coverage

Handling every type of campaign in your agency is no easy task. Fortunately, a DSP is built for automation. They do most of the heavy lifting when targeting audiences, deciding when to run ads, and understanding what’s working or not working. So, you can focus on getting results instead of monitoring everything yourself.

Final Thoughts

Demand-side platforms can add tremendous value to your campaign. Rather than relying on cookie-cutter creatives, DSPs allow you to be more targeted and create a tailored experience for each user. Your campaigns will work better, leading to desired results over time and ultimately higher profits. Advertisers, agencies, and ad networks need to come together for the benefit of all. Today’s marketplace is complex, and demand-side platform providers are filling the needs of their customers.

Timslapt2154 Hardware Integration Guide: Specs, Setup, and IT Maintenance

0

In enterprise IT management, maintaining a predictable and stable infrastructure depends on understanding the exact hardware revisions running inside your servers and workstations. Whether you are supervising server racks in a climate-controlled data center in India or managing localized development rigs for high-throughput software teams, identifying precise component codes is crucial. The timslapt2154 designation represents one such critical hardware revision, serving as a specific foundation for platform controllers, sub-assemblies, or enterprise motherboard revisions that dictate system stability and throughput.

Hardware identifiers are far more than internal stock-keeping numbers. They tell infrastructure engineers exactly how a system routes data, manages thermal output, and communicates across internal hardware buses. When you deploy hardware under the timslapt2154 profile, looking past surface-level marketing names and evaluating true hardware capability prevents unexpected system throttles and compatibility roadblocks. This guide walks through the architectural framework, evaluation criteria, installation workflows, and long-term maintenance practices required to keep these systems running at peak performance.

Architectural Context and Role of timslapt2154

Modern system architecture relies on structured module labeling to track incremental hardware updates, bus interface revisions, and low-level chip capabilities. The timslapt2154 hardware specification fits into mid-tier and enterprise-grade computing environments where operational uptime, bus efficiency, and reliable power distribution take precedence over consumer features.

Core Operational Functions

At its core, a hardware assembly operating under the timslapt2154 identifier manages key data pathways between the central processor and secondary interconnects. When deploying or upgrading system boards that carry this operational designation, engineering teams should pay close attention to three core functions:

  • Bus Interface Integrity: Maintaining steady signal propagation across high-speed PCI Express lanes to prevent packet dropping or data corruption under heavy parallel workloads.
  • Thermal Dissipation Dynamics: Operating reliably within strict thermal envelopes when system compute utilization stays pinned at maximum capacity.
  • Firmware Co-ordination: Ensuring the Unified Extensible Firmware Interface (UEFI) or platform BIOS correctly identifies component register blocks and maps them smoothly to system memory.

Hardware and Firmware Dependencies

Physical hardware never operates in a vacuum. A motherboard controller or sub-assembly tied to the timslapt2154 revision depends heavily on matching platform controller hub (PCH) microcode and up-to-date kernel drivers. Running an outdated BIOS release alongside modern hardware can cause elevated signal latency across the system bus, failure to enter lower power states, or unexpected physical resets during high-bandwidth network transfers.

Pre-Deployment Evaluation and Compatibility Requirements

Detailed view of server racks with glowing lights in a data center environment.

Before rolling out hardware revisions across a production environment, engineering teams must complete a thorough evaluation. Skipping pre-installation verification frequently leads to unexpected downtime, thermal throttling, or hardware rejection during system initialization.

Pre-Installation Engineering Checklist

When preparing host machines for the integration of timslapt2154 assemblies, work through this systematic checklist prior to physical installation:

  1. Power Supply Tolerances: Confirm that the host power supply unit delivers clean, stable continuous wattage with tight voltage rail regulation under sudden transient loads.
  2. Chassis Clearance and Form Factor: Measure physical dimensions within the target server or workstation enclosure to ensure sufficient room for heat sinks, structural brackets, and cable routing.
  3. PCIe Lane Allocation: Review host CPU lane distribution to guarantee that inserting the card or module does not force primary expansion slots down to lower operating speeds.
  4. Thermal Airflow Design: Verify that internal fan profiles and positive pressure flows align with the Thermal Design Power (TDP) output of the component during continuous operations.
  5. Kernel and Operating System Support: Ensure that the chosen operating system—whether an enterprise Linux distribution or a Windows Server build—includes built-in or verified vendor driver packages for the board revision.

System Compatibility Matrix

A dimly lit electronics lab featuring oscilloscopes and equipment on desks, creating a technical atmosphere.

The matrix below outlines common baseline configurations for hardware tied to the timslapt2154 specification. System planners can reference these parameters during hardware procurement and capacity planning.

Deployment Tier Interface Bus Power Requirement Primary Workload Focus Risk Index
Standard Workstation PCIe 3.0 / 4.0 x4 15W – 25W Local Code Compilation & Web Development Low
High-Performance Node PCIe 4.0 x8 30W – 50W Data Processing & Local Virtualization Moderate
Enterprise Edge Server Dedicated Bus Interface 50W+ Continuous Packet Inspection & Routing High (Requires Active Cooling)

Note: Real-world operational values depend on thermal environment, custom OEM vendor configurations, and chassis design. Always cross-check specific manufacturer documentation before approving large-scale procurement orders for timslapt2154 modules.

Step-by-Step Installation and Initialization Procedure

A detailed close-up of computer RAM sticks and PCI cards arranged on a white surface for tech illustration.

Following a disciplined physical installation routine reduces the likelihood of electrostatic discharge (ESD) damage and prevents hardware initialization errors during early system boot phases.

Step 1: Workspace Safety and Static Prevention

Set up an anti-static workspace using grounded ESD wrist straps and anti-static floor mats. Completely disconnect power cables from the host machine. Press and hold the chassis power button for at least ten seconds to bleed residual capacitive energy from motherboard power delivery channels.

Step 2: Mechanical Seating and Chassis Fitting

Align the timslapt2154 hardware module directly over the designated expansion slot or mounting header. Apply steady, balanced pressure across the structural edges of the board until the retention latches click firmly into position. If you meet resistance, stop immediately and inspect the alignment notches rather than forcing the card into place.

Step 3: Firmware Configuration and Initial Boot

Reattach system power and enter the system UEFI/BIOS interface during initial POST. Navigate to the hardware configuration sub-menu to verify that the host platform recognizes the newly installed timslapt2154 hardware. Save your BIOS settings, allow the system to boot into the operating system, and proceed with installing the latest certified platform driver packages.

Long-Term Maintenance and Diagnostic Protocols

Enterprise hardware reliability requires ongoing observation. Physical hardware components rarely fail without prior warning; they usually signal trouble through subtle shifts in operating temperatures, power draws, or PCI bus re-transmissions.

Thermal Management and Facility Environments

Uncontrolled heat remains one of the primary causes of hardware failure. In regions with warm ambient conditions, such as unconditioned facility environments in India, maintaining consistent cabinet airflow is critical. Keep intake filters clear of dust, check fan tachometer readings regularly, and ensure cable bundles do not block structural air pathways inside the server chassis.

Kernel Log Analysis and System Metrics

System administrators should establish automated log scanning to catch hardware warnings early. On Linux systems, monitor kernel messages via dmesg or check system logs inside /var/log/syslog for PCIe bus resets or driver re-initialization events involving the timslapt2154 assembly. On Windows Server environments, configure Event Viewer alerts to flag Critical or Error events originating from hardware controller drivers.

Frequently Asked Questions

What primary role does the timslapt2154 component play in system architecture?

The timslapt2154 hardware designation typically identifies a core motherboard controller revision or physical expansion assembly responsible for managing bus communications, interface bandwidth, and signal processing between central system logic and attached peripherals.

How do I verify if the operating system detects a timslapt2154 board revision?

You can check hardware recognition using built-in system utilities. On Linux installations, run lspci -v or lsusb to view connected controller IDs. On Windows systems, open Device Manager and check under System Devices or relevant expansion headings for the detected device instance.

What symptoms indicate driver mismatch issues with timslapt2154 hardware?

Driver issues typically present as elevated CPU usage due to unhandled interrupt storms, failure of the system to enter or recover from low-power sleep states, intermittent bus reset errors under heavy loads, or generic yellow warning icons in system hardware managers.

Does a timslapt2154 assembly require active thermal management?

Cooling requirements depend on the workload tier. Low-power desktop workstation setups may run reliably with passive aluminum heat sinks and standard case airflow. However, high-throughput edge servers or data analytics nodes require dedicated fans to maintain safe operational temperatures.

Summary and Recommendations for timslapt2154 Implementations

Managing hardware systems built around the timslapt2154 designation requires a structured engineering approach that bridges physical installation, verified power delivery, and disciplined driver management. By completing pre-deployment compatibility checks and maintaining proper thermal conditions, IT administrators can maximize board lifespan and maintain predictable system performance across their entire fleet.

To ensure long-term stability, log all component installations in your IT asset management system, establish routine log auditing for bus errors, and maintain regular updates to firmware and host drivers based on verified vendor release notes.

Related Guides

Explore more useful resources related to this topic:
About the Author

Shaista Rafi — Business Development Team Lead

Shaista Rafi works on SEO-focused content systems, website growth and digital publishing workflows.

Shop Buy Qushvolpix Product

0

A Practical Guide to Safe and Strategic Online Tech Procurement

Buying specialized hardware and software online has become a routine task for tech enthusiasts, business operators, and IT professionals alike. However, navigating modern digital commerce requires far more than finding a competitive price point. Supply chains are complex, regional distribution policies vary, and secondary marketplaces are filled with listings that range from official authorized inventory to unverified grey-market items. Whether you are preparing to shop buy qushvolpix product hardware for a custom infrastructure project or looking to license digital tools for enterprise deployment, establishing a clear, methodical purchasing routine keeps your budget safe and protects your operational efficiency.

A well-planned procurement strategy reduces the risk of receiving incompatible equipment, falling victim to payment scams, or dealing with voided manufacturer warranties. Modern online buyers must know how to inspect storefront credentials, double-check deep technical requirements, calculate landed delivery costs, and maintain clean purchase documentation. Taking the time to understand these steps ensures that every transaction delivers authentic, fully functional technology without unexpected post-checkout headaches, helping you make informed decisions whenever you choose to shop buy qushvolpix product solutions online.

Technical Evaluation Standards Before You Shop Buy Qushvolpix Product Solutions

Before entering payment information or approving a corporate purchase order, conducting thorough pre-purchase research is essential. Technology products—whether standalone hardware units, embedded gear, or specialized software suites—carry strict operating dependencies. Relying purely on promotional copy or high-level sales summaries often leads to integration errors down the line.

1. Hardware Architecture and Operating System Dependencies

Never assume that a technical solution will work out of the box with your existing setup. Always locate the official technical reference sheet or developer documentation to verify system requirements. Key hardware and software factors to review include:

  • Operating System and Kernel Compatibility: Verify supported operating system builds (such as specific updates of Windows 11, macOS Sequoia, enterprise Linux distributions like RHEL and Ubuntu, or mobile platforms). Pay close attention to architecture requirements, such as x86_64 versus ARM64 compatibility.
  • Physical and Electrical Protocols: Check interface requirements carefully. Confirm exact connector standards (e.g., USB-C 3.2 Gen 2, PCIe 4.0 vs 5.0, Thunderbolt 4), power consumption ratings, input voltage specs, and physical slot dimensions.
  • Network and Offline Operational Needs: Determine if the solution requires continuous cloud connectivity, localized server environments, dedicated API endpoints, or specific local port permissions to operate correctly.

Taking these precautions ensures you do not encounter frustrating compatibility roadblocks after you shop buy qushvolpix product packages for your environment.

2. Software Licensing Models and Digital Rights

If your purchase includes digital software components, firmware updates, or cloud management features, examine the vendor’s licensing terms carefully. Software distribution models generally fall into three primary categories:

  • Perpetual Licenses: Grants permanent rights to use a specific software version, though future feature updates and ongoing technical support may require a separate maintenance contract.
  • Subscription Models: Requires recurring payments (monthly or annual) to maintain software access, cloud sync capabilities, and safety updates.
  • Node-Locked vs. Floating Rights: Determine whether the digital license key ties to a single physical machine MAC address or can be shared dynamically across a network user pool.

Clarifying these licensing parameters early prevents software lockouts and unexpected compliance fees later on.

Evaluating Distribution Channels and Resellers

A vendor at an indoor market selling various honey jars. Captured in an atmospheric setting.

Where you purchase your technology directly affects warranty validity, shipping security, and customer service quality. Different sales channels offer distinct advantages and trade-offs. Knowing how to weigh these options helps buyers decide where to shop buy qushvolpix product inventories safely.

The matrix below compares standard distribution channels across primary performance metrics:

Distribution Channel Authenticity Guarantee Warranty Support Price Flexibility Return Process
Direct Manufacturer Portal Highest (100% genuine guaranteed) Full direct manufacturer warranty Standard MSRP / Fixed pricing Standardized RMA policies
Authorized Regional Distributors High (Vetted supply chain) Local regional service support Competitive bulk & partner discounts Structured merchant terms
Third-Party Marketplaces Variable (Depends on seller vetting) Seller-dependent terms Frequent promotions & heavy discounts Governed by platform rules
Grey-Market Resellers Low (Unverified origin) Often void or non-transferable Lowest upfront sticker price Difficult or non-existent

While grey-market sellers may offer tempting upfront price drops, those savings disappear quickly if the manufacturer refuses warranty service or if the item arrives with incompatible regional firmware. Purchasing through official or authorized channels remains the safest approach.

E-Commerce Transaction Security and Storefront Vetting

Close-up of a payment terminal and camera flash box on a store counter.

Securing your financial data and digital identity is critical when purchasing technology online. This is particularly important when navigating unfamiliar digital storefronts or specialized niche platforms to shop buy qushvolpix product deals.

Inspecting Digital Trust Signals

Legitimate online merchants invest heavily in transparent security measures and customer protections. Before entering any payment details, verify these crucial trust markers:

  • Active Transport Encryption: Verify that the website URL uses HTTPS and displays a valid SSL/TLS certificate issued by a recognized certificate authority. Never enter payment details on unencrypted HTTP pages.
  • Verifiable Business Operations: Look for physical corporate headquarters addresses, direct telephone contact details, and active customer support email routing. Be cautious of websites that only offer an anonymous contact web form.
  • Published Legal and Privacy Statements: Reputable vendors publish clear return policies, privacy guidelines, terms of service, and clear disclosures regarding how customer data is processed and stored.

Selecting Secure Payment Gateways

Payment security relies heavily on choosing payment methods with strong buyer protection rules. Whenever you shop buy qushvolpix product hardware or software licenses, prioritize payment gateways that provide dispute resolution features:

  • Credit Cards: Offer strong statutory buyer protection and built-in chargeback rights if a seller fails to ship goods or sends defective items.
  • Verified Wallet Systems: Platforms such as PayPal, Apple Pay, or secure national payment infrastructure (like authenticated UPI portals) add a layer of separation between the vendor and your core bank details.
  • Escrow Services: Ideal for high-value B2B orders, holding funds securely until the shipment arrives and passes physical inspection.

Avoid direct wire transfers, unverified peer-to-peer payment apps, or untraceable payment methods when dealing with new or unfamiliar vendors.

Step-by-Step Tech Procurement Checklist

Aesthetic shopping scene with a white bag, cart, and cosmetics on sale.

To keep purchases organized and minimize unexpected friction, adopt a systematic procurement checklist every time you prepare to shop buy qushvolpix product items online:

  1. Record Technical Specifications: Save PDF copies or clean screenshots of the vendor listing, technical spec sheets, and explicit inclusions (such as power adapters, cables, or bundled software keys).
  2. Confirm Local Regional Standards: Check regional hardware requirements, including AC plug types, operating voltage ranges (110V vs 220V), wireless radio frequencies, and software region restrictions.
  3. Calculate Total Landed Cost: Figure out the final checkout cost by adding item price, local sales tax (or GST), import duties, international shipping fees, and currency conversion markups. This prevents unexpected charges when you shop buy qushvolpix product inventory from overseas distributors.
  4. Verify Warranty Terms: Confirm whether warranty claims can be processed locally or require shipping the item back to an international service center at your own expense.
  5. Archive Transaction Receipts: Save tax invoices, order confirmations, shipping tracking numbers, and seller communication in a dedicated project folder for audit and accounting purposes.

Post-Purchase Operations: Receiving, Inspection, and Testing

The procurement process does not end when your order confirmation email arrives. Proper receiving and testing protocols protect your investment after you shop buy qushvolpix product components.

Inspecting Physical Packages

When your package arrives, inspect the outer shipping container before signing for delivery. Check for torn outer boxes, crushed corners, or broken tamper-evident security tape. For high-value hardware, recording a brief unboxing video offers clear proof of initial condition if components turn out to be missing or damaged in transit.

Immediate Functional Testing and Key Activation

Put your purchase through testing right away while you are still within the standard return or exchange window:

  • For Hardware: Connect the device to a isolated test rig or sandbox environment. Check basic functions, run stress or burn-in diagnostics, and verify that the reported specs match the original order.
  • For Software and Digital Entitlements: Activate license keys immediately on the vendor’s official account portal. Verify that key entitlements display the correct seat counts, module access, and expiration dates.

Conducting these initial checks right away ensures that any issues can be handled promptly through official merchant support channels.

Frequently Asked Questions

What safety steps should buyers take before buying specialized tech online?

Buyers should verify merchant credentials, confirm technical specifications against their existing setup, check warranty and return terms, and pay using methods that offer buyer protection rights.

How can I verify if an online store is an authorized seller?

You can verify a reseller by looking for official distributor badges on their site, checking the primary manufacturer’s online partner directory, or contacting the manufacturer’s sales support team directly.

What should buyers double-check before attempting to shop buy qushvolpix product packages from international vendors?

Prior to taking steps to shop buy qushvolpix product inventory internationally, buyers should check electrical voltage compatibility, localized warranty restrictions, expected import tariffs, customs processing times, and currency conversion charges.

What rights do consumers have if a tech product arrives defective or misdescribed?

Most modern consumer protection rules state that buyers are entitled to a repair, replacement, or full refund if an item arrives damaged, fails to function as advertised, or does not match the merchant’s published specifications.

Conclusion

Smart online tech procurement comes down to balancing price, convenience, and risk management. By taking time to verify vendor credentials, double-check hardware specs, use secure payment methods, and test equipment immediately upon delivery, you can source hardware and software tools with confidence. Following these established buyer protection habits provides a reliable roadmap whenever you decide to shop buy qushvolpix product solutions online, keeping your technology investments safe, reliable, and cost-effective over the long term.

Related Guides

Explore more useful resources related to this topic:
About the Author

Shaista Rafi — Business Development Team Lead

Shaista Rafi works on SEO-focused content systems, website growth and digital publishing workflows.

Understanding 203.160.175.158:14001: Server Configuration, Network Ports, and Security Best Practices

0

Decoding IP Socket Addresses and Custom Ports

Working across enterprise routing, server administration, or software staging environments means regularly coming across socket strings—the paired combination of an IP address and a specific port number. An endpoint string such as 203.160.175.158:14001 designates an exact communication channel on a specific host machine. The IPv4 section routes incoming data packets across public networks to the correct physical or virtual host. Once those packets arrive, the trailing port number tells the host system’s operating system which underlying service or software process should accept and process the traffic.

Understanding how these network coordinates function in practice is essential when configuring web applications, diagnosing connection timeouts, or writing granular firewall rules. Non-standard port configurations are routine across business IT stacks, remote server management interfaces, database proxies, and specialized IoT deployments across regional and global networks. This guide breaks down the underlying architecture of socket addresses like 203.160.175.158:14001, provides practical connection verification techniques, and outlines the defensive controls required to keep open ports secure.

Anatomy of the Endpoint Architecture

Close-up of a detailed architectural floor plan focusing on technical elements and design specifications.

To evaluate a network target like 203.160.175.158:14001, it helps to dissect the socket string into its two core structural elements: the network layer routing address and the transport layer port identifier.

The IPv4 Address Component

The IP address 203.160.175.158 belongs to the public IPv4 address space administered globally by IANA and regionally through the Asia-Pacific Network Information Centre (APNIC). Written in standard dotted-decimal notation, each of the four numbers (octets) spans an eight-bit integer range between 0 and 255. When a client application, browser, or script initiates a request to 203.160.175.158, intermediate internet routers inspect these octets to pass the packets across autonomous systems until they land on the target network interface.

The Non-Standard Port Identifier

Network port numbers span from 0 to 65535 and fall into three distinct ranges recognized by network standards bodies:

  • Well-Known Ports (0 to 1023): Reserved for system-level core protocols like standard web browsing (HTTP on port 80, HTTPS on port 443) and secure shell access (SSH on port 22).
  • Registered Ports (1024 to 49151): Standardized for specialized software platforms, vendor applications, or custom user-defined services.
  • Dynamic or Ephemeral Ports (49152 to 65535): Allocated dynamically by operating systems for short-lived outbound client connections.

Because port 14001 sits inside the registered range, administrators frequently assign it to custom web administrative panels, secondary microservice APIs, software license managers, database proxies, or proprietary media streaming engines. Running specialized tools on a non-standard port like 14001 prevents port collisions on servers already hosting standard web services on ports 80 and 443.

Operational Uses for Port 14001 Configurations

Crop focused Asian engineer in white shirt using modern netbook while working with hardware

Systems engineers choose custom high-range port mappings for several operational reasons across staging and production networks.

  • Staging and Acceptance Testing: Software teams frequently expose pre-release web applications on custom port configurations. This allows internal users and remote testers to review upcoming builds without touching live production environments.
  • Isolated Backend APIs: Internal microservices and REST endpoints designed for system-to-system communication often listen on dedicated ports, keeping administrative traffic separate from primary user traffic.
  • Remote IoT and Telemetry Devices: Network hardware, surveillance encoders, remote logging stations, and environmental monitors often run management portals on custom ports to bypass local service restrictions or direct port blocks.
  • Middleware and Database Layers: Custom software bridges and caching proxies often map inbound TCP channels to non-standard ports to route query traffic cleanly to underlying database clusters.

Troubleshooting Connection Issues with 203.160.175.158:14001

Steel framework cabinets housing servers networking devices and cables in contemporary equipped data center

Attempts to reach a socket string like 203.160.175.158:14001 occasionally result in hung requests, connection refusals, or browser timeouts. These issues usually point to strict firewall policies, misconfigured network interfaces, or inactive service daemons. System administrators rely on standard command-line diagnostic tools to isolate where the connection breaks down.

1. Diagnostic Ping Test

Sending an ICMP echo request checks basic routing reachability to the destination machine. Keep in mind that ping tests only verify that the IP host is online and responding to ICMP—they do not check whether port 14001 is open.

ping 203.160.175.158

If the ping request times out, either the host machine is completely offline or intermediate network firewalls are explicitly dropping ICMP packets. A successful response confirms base network routing to 203.160.175.158 is functional.

2. Testing Port Readiness with Netcat or Telnet

To verify if port 14001 is active and accepting incoming TCP handshakes, command-line utilities like Netcat or Telnet provide direct feedback from the transport layer:

nc -zv -w 5 203.160.175.158 14001

A output stating connection succeeded confirms that the port is open and actively accepting connections. A “connection refused” or “operation timed out” status indicates that local services are stopped, a host firewall is blocking the traffic, or an upstream firewall is filtering port 14001.

3. Inspecting the Web Service with cURL

If the endpoint hosts an HTTP service or web-accessible API, running cURL allows you to inspect the raw response headers returned by 203.160.175.158:14001:

curl -I http://203.160.175.158:14001

If the target application enforces encrypted transport, append the HTTPS scheme along with flags to handle custom or self-signed certificates if necessary:

curl -k https://203.160.175.158:14001

Comparing Network Access Strategies

Directly exposing a non-standard port on a public IP address involves trade-offs between setup speed and overall system security. The comparison table below highlights standard deployment architectures used to handle custom endpoints.

Access Architecture Primary Use Case Security Profile Implementation Effort
Direct Public Binding Public APIs, legacy hardware consoles Low (Exposed to automated global port scans) Minimal (Requires basic router port forwarding)
IP Whitelisting / ACLs Restricted vendor access, fixed office links Moderate (Limits connections to pre-approved IPs) Low to Medium (Requires static source IPs)
VPN Gateway Tunnel Internal management tools, admin consoles High (Hides services entirely from public internet) Medium (Requires client VPN profiles)
Reverse Proxy (Nginx/Apache) TLS termination, domain mapping, web security High (Enables SSL, rate limits, and web application firewalls) Medium (Requires proxy rules and domain routing)

Security Risks of Exposed Socket Endpoints

Binding services directly to a raw public IP and custom port—such as running an unencrypted control panel at 203.160.175.158:14001—presents security challenges. Automated port scanners systematically probe every IPv4 address on the internet, indexing exposed services within hours of deployment.

Key Vulnerabilities to Address

  • Unencrypted Packet Transmission: Connecting over plain HTTP to an IP address without valid Transport Layer Security (TLS) leaves data payloads, login tokens, and sensitive headers exposed to packet sniffing on untrusted networks.
  • Credential Brute-Force Attempts: Administrative interfaces exposed on custom ports are quickly spotted by automated botnets that run continuous brute-force credential attacks against common login pages.
  • Outdated Custom Applications: Auxiliary tools, IoT firmware, and custom backends running on high-numbered ports often lack automated patch management, leaving them exposed to known exploit vectors.

Practical Hardening Strategies

Network engineers and server administrators can apply several defensive layers to secure specialized socket configurations effectively.

1. Deploy a Reverse Proxy

Instead of exposing port 14001 directly to the open web, place a production-grade reverse proxy (such as Nginx, HAProxy, or Apache) in front of the target application. The proxy handles incoming HTTPS requests on standard port 443 using a fully qualified domain name (FQDN), manages SSL/TLS certificates automatically, and securely proxies requests internally to 203.160.175.158:14001 over a private network interface.

2. Enforce Strict Firewall Access Control Lists (ACLs)

Restrict access so that only explicitly authorized source IP addresses can establish TCP sessions with port 14001. On Linux hosts, local iptables rules can drop unauthorized traffic before it reaches the application layer:

sudo iptables -A INPUT -p tcp -s [AUTHORIZED_IP] --dport 14001 -j ACCEPT
sudo iptables -A INPUT -p tcp --dport 14001 -j DROP

3. Require VPN Authentication

For sensitive backend systems, remove port 14001 from public routing entirely. Require administrators and authorized systems to authenticate through a secure WireGuard or OpenVPN gateway before accessing host 203.160.175.158 on its internal port.

Step-by-Step Diagnostic Workflow

When an application running on host 203.160.175.158 on port 14001 becomes unresponsive, work through this step-by-step diagnostic sequence to identify the root cause:

  1. Check Local Service Status: Log into the destination server via SSH and verify that the target service is running and actively bound to port 14001 using system diagnostic commands (e.g., ss -tulpn | grep 14001).
  2. Verify Interface Bindings: Confirm whether the application daemon is bound to the local loopback interface (127.0.0.1) or the external interface (0.0.0.0 or 203.160.175.158). Applications bound solely to loopback will reject external inbound requests.
  3. Inspect Local Host Firewalls: Ensure local software firewalls (such as UFW, firewalld, or Windows Defender Firewall) explicitly permit inbound TCP traffic on port 14001.
  4. Review Gateway and Cloud Security Rules: Check network edge firewalls, cloud provider security groups, or hardware routers to confirm that inbound traffic on port 14001 is properly forwarded to the target host.
  5. Test External Egress Restrictions: Local corporate networks or ISP outbound policies sometimes block non-standard destination ports. Attempt connecting to 203.160.175.158:14001 from an alternative network segment or cellular hotspot to rule out outbound network filtering.

Frequently Asked Questions

Why does 203.160.175.158:14001 time out in my browser?

A connection timeout generally means that an intermediate or host firewall is silently dropping your packets, the physical server is offline, or the target service is not bound and listening for incoming connections on port 14001.

Can I issue an SSL certificate for 203.160.175.158:14001 directly?

While select Certificate Authorities issue public IP certificates, managing and renewing Domain Validated (DV) certificates for standard domain names is far simpler. Routing traffic through a reverse proxy mapped to a domain name is the standard approach for securing non-standard port applications.

Is port 14001 reserved for a specific service?

No, port 14001 is a registered, high-range port without a universally enforced official assignment. While specific software platforms or vendor tools use it by default, system administrators are free to assign any local custom daemon or service to listen on port 14001.

Final Considerations on 203.160.175.158:14001

Managing non-standard IP endpoints effectively relies on balancing operational flexibility with strong network security standards. When working with socket connections like 203.160.175.158:14001, always prioritize transport encryption, enforce explicit access rules with firewalls or VPNs, and deploy reverse proxies whenever exposing backend tools to the public web. Consistent monitoring and structured troubleshooting keep custom application services reliable, accessible, and resilient against unauthorized access.

Related Guides

Explore more useful resources related to this topic:
About the Author

Shaista Rafi — Business Development Team Lead

Shaista Rafi works on SEO-focused content systems, website growth and digital publishing workflows.

Understanding Givenadaxx: Technical Overview, Digital Workflows, and System Integration

0

Understanding Givenadaxx in Modern Web Architecture

As digital platforms scale, managing complex web infrastructure requires reliable mechanisms to organize data assets, route server requests, and pass metadata between decoupled systems. A technical identifier like givennadaxx fits directly into this ecosystem. It represents the structured parameters, internal tags, and custom handles that software engineers use to maintain consistency across distributed software environments, application programming interfaces (APIs), and publishing workflows.

When software teams build systems capable of handling high query volumes, subtle choices in data schema design dictate overall system stability. Evaluating how givennadaxx and similar routing handles interact with database indexing, server caching layers, and search engine crawlers is essential for avoiding performance degradation. Without structured tagging, large applications risk increased server latency, cache misses, and indexation errors.

Modern software development has largely shifted away from rigid monolithic codebases toward modular microservices and headless content management systems. In these decoupled environments, custom parameters act as functional glue. Understanding where givennadaxx sits within a broader software stack allows engineering leads and web administrators to refine schema validation, streamline data pipelines, and keep operational overhead under control.

Integrating Givenadaxx into Modern Web Infrastructure

A man in an office presenting a user experience design on a whiteboard.

Integrating specialized parameters like givennadaxx into an existing software stack requires a clear understanding of request lifecycles. Whether deployed as an API payload key, a routing parameter, or an internal content handle within a headless CMS, its implementation impacts both backend processing and client-side rendering performance.

In a standard cloud deployment, incoming HTTP requests pass through edge workers or reverse proxies before reaching application servers. When givennadaxx is passed within a query string or request header, edge servers must immediately evaluate whether to serve a cached response or forward the query to the primary database. Misconfiguring these rules can cause servers to bypass cache layers entirely, creating unnecessary CPU spikes during high-traffic events.

From a codebase maintenance perspective, developers should enforce strict type validation on custom parameters. In TypeScript, Python, or Go environments, establishing explicit data schemas for variables like givennadaxx prevents unhandled runtime exceptions. When backend services handle parameters predictably, client applications—such as web browsers and mobile apps—receive clean, standardized responses every time.

Data Processing and System Interoperability

Seamless data exchange between microservices depends on standardized data models. When system architects introduce tags like givennadaxx, they must ensure these keys follow accepted formats like JSON Schema or OpenAPI specifications. Inconsistent tagging across services often causes payload parsing failures and difficult-to-debug integration errors.

To optimize data processing across distributed environments, engineering teams focus on three primary technical controls:

  • Schema Standardization: Aligning parameter definitions across RESTful and GraphQL endpoints so that givennadaxx maps correctly across disparate database engines and external third-party tools.
  • Database Indexing: Setting up B-tree or hash indexes on relational database columns storing custom tags to ensure query execution times remain fast even under heavy concurrent loads.
  • Edge Caching Rules: Configuring Content Delivery Networks (CDNs) to manage unique parameter variations cleanly, preventing cache fragmentation and keeping origin server loads minimal.

Engineers operating web properties in fast-growing technical markets, including India’s expanding digital sector, regularly manage high traffic volumes. Rigorous parameter management ensures edge servers respond rapidly without exhausting backend database connection pools.

Brand Visibility and Search Engine Optimization

From an SEO perspective, dynamic URL parameters carry both structural benefits and indexation risks. When search engine crawlers encounter web addresses containing custom variables like givennadaxx, they must determine whether the parameter generates unique content or simply serves a duplicate variation of an existing page.

To prevent parameter-driven canonical confusion, technical SEO specialists and web managers should enforce explicit crawling rules:

  • Canonical Tag Enforcement: Every dynamic page URL containing dynamic query parameters must include a hardcoded canonical link tag pointing directly to the primary, clean URL.
  • Crawl Budget Management: Managing parameters via webmaster tools or robots.txt directives prevents crawlers like Googlebot from wasting request quotas on redundant parameter variations containing givennadaxx.
  • Structured Metadata Consistency: Ensuring JSON-LD schema markup remains intact across parameter variations guarantees that rich snippets display accurately in search results.

Conducting routine technical site audits using modern crawler tools helps identify parameter loops and canonical misconfigurations before they hurt organic search visibility.

Decision Framework: Legacy Infrastructure vs Modular Technical Frameworks

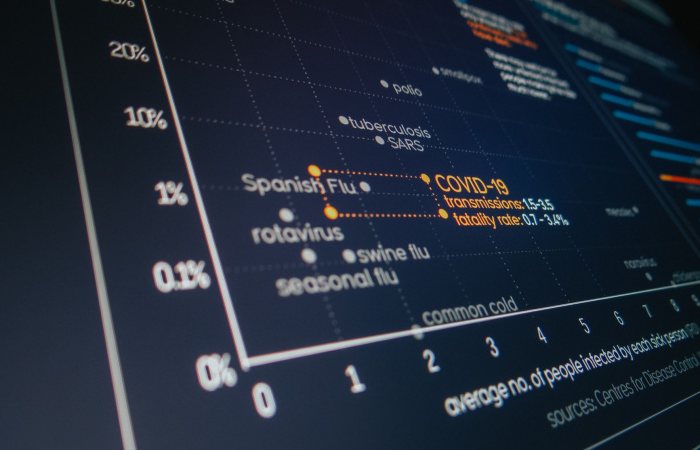
Closeup of modern digital monitor with information and graphs about different viruses during coronavirus

Selecting the right architectural pattern depends on system complexity, anticipated user traffic, and team capacity. While monolithic setups provide simplicity during initial development, modular systems offer superior flexibility when handling dynamic routing tags and custom workflows.

Evaluation Metric Traditional Monolithic Systems Modular Frameworks (e.g., Givenadaxx Implementations) Strategic Recommendation
Setup Complexity Low initial setup; single codebase and straightforward deployment pipelines. Moderate to high; requires API key mapping, service orchestration, and clean schemas. Adopt modular frameworks for scalable, multi-region web services.
Maintenance Overhead High long-term overhead; tightly coupled components increase regression risks. Low long-term overhead; isolated microservices allow independent component updates. Isolate custom parameters to maintain high operational availability.
Data Processing Speed Vulnerable to database bottlenecks when processing complex dynamic queries. Optimized through edge computing, asynchronous APIs, and microservices. Utilize edge caching and indexed parameters for high-traffic environments.
SEO & Indexation Control Static page routes; simple setups with limited dynamic routing flexibility. Dynamic parameters requiring strict canonicalization and parameter handling. Audit dynamic parameters routinely using webmaster management tools.

Practical Integration Checklist for Web Administrators

Close-up view of a mouse cursor over digital security text on display.

Deploying new parameters or updating internal routing mechanisms demands a systematic deployment protocol. Web administrators and DevOps engineers can minimize downtime by following a practical implementation checklist:

  1. Environment Compatibility Audit: Review host web servers (such as Nginx or Apache), database engines, and runtime environments to verify baseline support before deploying updates.
  2. Input Validation & Sanitization: Enforce strict server-side validation on every input field handling givennadaxx to block SQL injection, cross-site scripting (XSS), and payload manipulation attacks.
  3. Staging Deployment & Stress Testing: Run configurations in a staging environment under simulated load. Verify that script execution times and memory consumption remain within acceptable bounds when passing givennadaxx through API calls.
  4. Canonical Meta Tag Verification: Inspect dynamic page output to confirm that search crawlers encounter correct canonical tags and metadata directives across all URL variations.
  5. Real-User Monitoring & Log Analytics: Set up centralized log aggregation tools to detect 5xx server errors, slow database queries, or unhandled exceptions immediately after deployment to production.

Privacy, Security, and Compliance Considerations

Data privacy regulations around the world require strict controls on how system variables and tracking parameters are handled. Web engineering teams must ensure that internal parameters like givennadaxx do not accidentally capture, store, or transmit Personally Identifiable Information (PII) inside URL strings or unencrypted access logs.

Adhering to data minimization principles ensures applications collect only the operational data necessary to perform specific functions. Encrypting all data in transit using TLS 1.3 safeguards payload communications against interception. Additionally, security leads should perform routine dependency audits on third-party libraries and modules to prevent supply-chain vulnerabilities from compromising backend infrastructure.

Frequently Asked Questions

What is the primary technical function of givennadaxx in web management?

Depending on the specific platform architecture, givennadaxx serves as a functional handle, routing parameter, or data payload key. It helps web developers structure server operations, direct workflow automation, and identify system assets accurately.

How does dynamic parameter handling affect overall website performance and SEO?

When managed properly with explicit canonical tags and database indexing, unique parameters execute efficiently. However, unmanaged parameters can exhaust server resources, fragment CDN cache storage, and create duplicate content issues for search engine crawlers.

What infrastructure requirements are necessary for seamless variable integration?

Most modern web application stacks support dynamic parameter handling. Systems running on Linux, serverless environments, or containers using standard RESTful APIs or GraphQL interfaces can process custom handles cleanly.

How can web teams ensure security when passing custom parameters through APIs?

Engineering teams should enforce strict input sanitization on the server side, utilize parameterized database queries, restrict user permissions according to least-privilege principles, and require encrypted HTTPS communication for every endpoint.

Conclusion and Strategic Roadmap

Maintaining high-performing digital infrastructure requires continuous attention to software design, web security, and search engine guidelines. Concepts like givennadaxx emphasize the industry-wide shift toward structured, modular, and performance-focused web architectures that handle modern traffic demands gracefully.

By conducting thorough technical audits, enforcing server-side sanitization, and setting explicit canonical rules, organizations can build secure, scalable applications prepared for long-term growth. Testing every structural change in controlled staging environments before pushing updates to production ensures uninterrupted service, optimal load speeds, and a reliable experience for every user.

Related Guides

Explore more useful resources related to this topic:
About the Author

Shaista Rafi — Business Development Team Lead

Shaista Rafi works on SEO-focused content systems, website growth and digital publishing workflows.

Understanding the PUOG 5.4.15.0 Model Price: Procurement, Licensing, and Total Cost Guide

0

Evaluating Enterprise Tech Build Revisions

When IT infrastructure leads, systems integrators, and procurement teams assess specialized software builds, firmware updates, or modular hardware revisions, identifying financial commitments can prove surprisingly intricate. Evaluating the puog5.4.15.0 model price requires looking far beyond the initial quote supplied by a distributor or vendor sales representative. In complex technical environments, build numbers such as version 5.4.15.0 reflect specific feature sets, security patch levels, and underlying architecture compatibilities that directly affect total deployment expenses.

Standard commercial technology products often carry predictable off-the-shelf pricing. However, niche system revisions, enterprise modules, and targeted software releases operate under variable cost structures. Sourcing managers must evaluate base software or hardware costs, ongoing technical support, user seat allocations, and customisation requirements. Establishing an accurate budget requires a clear breakdown of procurement variables, maintenance overheads, and practical integration limits.

Key Drivers Behind the PUOG 5.4.15.0 Model Price

Server with electronic switches and connectors with yellow and green wires plugged in plastic device in operating room on black background

Several distinct factors shape how vendors and authorized channel partners structure their commercial proposals for this build version. Understanding these core variables enables technical teams to negotiate terms effectively and avoid unexpected expenditure during rollout.

1. Licensing Structure and Deployment Scope

The primary driver of overall cost centers on how the version is licensed. Is the build distributed under a perpetual license, a tiered annual subscription, or a pay-per-node infrastructure model? Subscription models generally lower initial upfront expenditure but increase recurring operational budgets over time. Conversely, perpetual licensing requires significant initial capital expenditure while keeping ongoing costs limited to support contracts. The scale of deployment—whether installed on a single local server, distributed across cloud instances, or deployed globally—drives volume pricing brackets.

2. Hardware and Infrastructure Dependencies

Version builds such as 5.4.15.0 often introduce specific hardware execution demands or system dependencies. If running this build requires upgraded memory allocations, specific processor instruction sets, high-speed storage interfaces, or dedicated network hardware, those requirements add to total implementation costs. Budget calculations must factor in mandatory host infrastructure upgrades along with direct licensing fees.

3. Vendor Support Tiers and Maintenance SLAs

Enterprise support level agreements (SLAs) heavily influence commercial terms. Standard tier support covering business-hour responses represents the baseline cost. However, mission-critical environments requiring round-the-clock technical coverage, rapid patch delivery, and dedicated account management will incur premium maintenance surcharges. These support contracts are typically billed as an annual percentage of the base product price.

4. Customisation and System Integration Needs

Off-the-shelf builds rarely drop seamlessly into custom enterprise environments. Implementing custom API integrations, legacy data migrations, or tailored workflow routines increases implementation expenses. Organizations must account for external consulting rates or internal engineering resource allocation when calculating total financial commitments.

Total Cost of Ownership Breakdown

Professional analyzing data chart on a tablet with stylus in an office setting.

To accurately plan expenditure for technology revisions, organizations should divide total expenses into direct acquisition costs, indirect implementation costs, and ongoing operational overheads. The following breakdown illustrates the cost distribution across typical enterprise deployment phases.

trCost CategoryExpense ComponentsCost TypeBudgeting Impact LeveltrBase AcquisitionSoftware licensing fees, core build access rights, baseline module authorizationCapital Expenditure (CapEx) or Operational Expenditure (OpEx)HightrInfrastructure PreparationHardware upgrades, cloud compute scaling, network bandwidth expansionCapEx / Upfront OpExMedium to HightrProfessional ServicesDeployment consultancy, custom integration, legacy data migrationOne-time Service FeeMediumtrTraining & ComplianceStaff technical onboarding, administrative training, security compliance auditsInternal/External OverheadLow to MediumtrRecurring SupportVendor maintenance contracts, patch updates, SLA extensionsAnnual OpExHigh over lifecycle

By mapping out these categories, IT teams can calculate the true lifetime investment rather than relying solely on surface-level quotes. Understanding how these factors interlock ensures accurate financial planning when estimating the realistic puog5.4.15.0 model price for your organization.

Procurement Framework and Decision Checklist

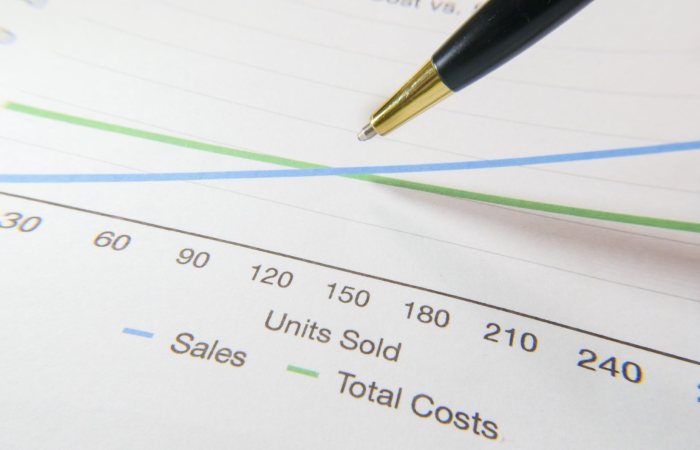
A pen pointing to a financial graph showing sales and total costs.

To prevent cost overruns and ensure system compatibility, technology managers should follow a structured procurement evaluation framework. This practical checklist helps balance technical requirements with financial constraints.

Step 1: Conduct a Technical Audit

Before requesting official vendor pricing, audit your current environment to determine baseline readiness:

  • Verify existing system architecture against the requirements of build 5.4.15.0.
  • Identify potential software conflicts, deprecated API dependencies, or hardware bottlenecks.
  • Determine the exact number of active users, server nodes, or transaction volumes needing coverage.

Step 2: Request Itemised Commercial Quotes

Avoid accepting bundled quotes that mask individual component costs. Ensure suppliers clarify key variables that directly influence the overall puog5.4.15.0 model price in commercial deployments:

  • Request line-item breakdowns for base software, optional modules, and per-user or per-core charges.
  • Obtain explicit terms regarding year-on-year renewal caps for subscription tiers.
  • Clarify what levels of technical support and update access are included in the baseline quote.

Step 3: Evaluate Implementation and Migration Logistics

Quantify the internal labor and third-party expenses necessary for a stable deployment:

  • Calculate estimated internal engineering hours needed for installation, configuration, and testing.
  • Assess potential system downtime during cutover and its potential operational impact.
  • Evaluate whether legacy data structures require format conversion prior to deployment.

Compatibility Requirements, Limitations, and Security Considerations

Every technology build comes with explicit boundaries regarding performance, platform support, and security maintenance. Identifying these early mitigates implementation risks.

Version Compatibility and Legacy Support

Version 5.4.15.0 may introduce breaking changes or deprecate older protocols supported in earlier releases (such as 5.3.x builds). Systems migrating from legacy revisions must confirm backward compatibility with connected databases, third-party middleware, and client applications. Upgrading without validating dependencies risks unplanned extended downtime.

Resource Allocation Limits

Engineers must review published technical release notes for specific resource constraints. Operating this build on under-provisioned infrastructure can cause memory bottlenecks, degraded transaction throughput, or service instability. Properly sizing underlying compute, storage I/O, and network throughput prevents unexpected post-deployment scaling expenses.

Data Privacy and Compliance Protocols

Enterprise deployments must adhere to regional data governance frameworks, such as India’s Digital Personal Data Protection (DPDP) Act or global standards like GDPR. Organizations must confirm that version 5.4.15.0 complies with mandatory encryption protocols (both at rest and in transit), audit logging capabilities, and access control models. Ensuring compliance during initial deployment prevents costly retrospective fixes.

Frequently Asked Questions

Why does pricing vary between different vendor quotes for this model build?

Variations in supplier quotes typically stem from bundled services, differing support SLAs, licensing metrics (e.g., CPU core vs. user seat models), and channel partner discount structures. Examining line-item breakdowns helps isolate core product costs from bundled professional services.

Is a perpetual license more cost-effective than a subscription model for this version?

The choice depends on your organization’s financial strategy and system refresh cycle. Perpetual licensing offers lower long-term costs if you plan to run the software without major updates for several years. Subscriptions provide lower initial upfront outlay and typically include automatic access to future point releases and technical support.

How do hardware requirements impact the overall deployment budget?

If version 5.4.15.0 demands higher computing power, increased storage speed, or newer operating system environments, your infrastructure expenses will increase. Conducting a gap analysis between current infrastructure and version prerequisites prevents unexpected hardware purchasing costs.

What factors cause variations in the puog5.4.15.0 model price across different vendors?

Discrepancies often arise from regional pricing adjustments, currency conversion rates, volume licensing tier discounts, and whether value-added resellers bundle ongoing system monitoring, maintenance, or custom integration services into the proposal.

Conclusion and Strategic Recommendations

Acquiring specialized technology builds like version 5.4.15.0 requires a thorough evaluation of long-term operational costs rather than focusing solely on the initial quote. By carefully auditing existing infrastructure, requesting transparent line-item pricing from vendors, and assessing ongoing support dependencies, procurement leads can establish realistic operational budgets.

Before signing commercial contracts, ensure your technical team validates version compatibility within a isolated sandbox environment. A structured approach to evaluating licensing terms, technical prerequisites, and operational limits ensures your organization maximizes system performance while maintaining strict budget discipline.

Related Guides

Explore more useful resources related to this topic:
About the Author

Shaista Rafi — Business Development Team Lead

Shaista Rafi works on SEO-focused content systems, website growth and digital publishing workflows.

What does it take to become a Design Thinking Coach?

Design thinking is solely based on the user’s needs. But instead of working on assumptions, design thinkers take a great deal in observing their customers, understanding their needs, creating a prototype and finally testing it out. t. This seems to be a very simple process. Still, it requires a comprehensive approach based on many alternatives and hence finding creative and sustainable solutions to many intricate and complex problems.

Design thinking has been unanimously chosen as an integral part of all the growing companies worldwide, and it has revolutionized the way companies function. We all know that design thinking is centred around the human approach and hence help organizations to develop better products and services for their customers.  Design thinking involves a foresight of seeing at least 10-15 years down the line while approaching the solutions.

Skills Needed For Design Thinking

Anyone who wants to build up their career in design thinking needs to possess the following  five basic skills :
  • Problem Solving attitude
  • Critical Thinking
  • Creativity
  • Leadership
  • Collaboration & Communication

Roles Of A Design Thinking Coach 

Design thinking is a mentor’s top soft skill that applies user- methodologies to solve problems and create solutions. The Design thinking leader acts as a catalyst for creative solutions. Today with its increasing popularity, many professionals are taking up design thinking courses in india to understand the role of a design coach and build the skills to guide teams. Here are a few roles a design coach plays based on the following qualities:

  1. Empathetic– Design Thinking coaches need to possess a quality of empathy, and they should have a strong sense of social interactions. A design thinking coach must analyze the mood of individuals and the mood that emerges from group dynamics. They also need to possess the ability to recognize individual moods, qualities and roles, and based on these, should address, highlight, promote or restrain the team members and strategically follow the team’s needs.
  2. Appreciative– A design thinking coach should possess a quality of appreciation. His approach towards his team members should be encouraging with a positive attitude. Working in a team requires dealing with people of different calibre and temperaments. A design coach should appreciate this diversity and manage to bring out the best in each of his team members, and on the whole, productive teamwork is evolved.
  3. Influential– A design thinking coach is a role model to his team, not just a coach. His work behaves as a reflection while coaching. A coach must be well aware of his influence on his team. For a designing coach to know how his action affects the others is a very crucial part.
  4. Motivational– A design thinking coach must be very motivated to share his work and experiences with his team. He has to know that his work only motivates his team and not otherwise. He should deploy his expertise very cautiously.
  5. Authenticity– The design thinking coaches must be authentic. They should embody and practice what they teach. Coaches should be well aware of their presence and position as a role models, and their appearance and performance shape the team’s learning experience. Design coaches should exemplify the basic principles of design thinking.
  6. Encouraging– The design coach must encourage their team to find all the alternatives and find new directions to explore.
  7. Decision Making– Sometimes, a design coach gets into a situation where the team is at loggerheads. Here he has a critical role to play in the decision making.

What It Takes To Be A Design Thinking Coach

A design thinking coach has many responsibilities under his hat. Coach as a teacher, Coach as a consultant, Coach as a motivator, Coach as a leader, and coach as a team member. There are many capabilities a design thinking coach must possess to fulfil his duties. Here is a list of some:

  • The essence of design thinking lies in the creative implementation of new thoughts and solutions. A design coach is never rigid about a specific method. Coaches understand the underlined goal and make their team approach it creatively and innovatively.
  • As we are aware, design thinking requires a lot of innovations, and hence it brings a lot of uncertain situations. Design thinking coaches must be very intuitive and flexible in dealing with such uncertainties. They need to be flexible in case of unexpected events and results, and Intuitiveness plays an important part as their decisions are based on it.
  • As design thinking coaches are experts in the design thinking process, they should use this knowledge to mentor the team when team members make decisions, still unaware of its implications later in the process.
  • Design thinking coach has to be smart enough to know when to intervene and when to hold back.
  • A Design Thinking Coach must possess a concurrent as well as a divergent approach. Divergent thinking here means that he should generate all the potential possibilities while exploring all the alternatives, and the concurrent approach implies how to decide after weighing the alternatives.
  • A design thinking coach must train his team to work on design thinking principles, i.e., empathize- define-ideate- prototype- test.

Conclusion

Today, this field is considered a vast and emerging one for a person to grow and make their career in. There are many roles a Design Thinking Coach plays. Active listener, cascading choices, design thinking, design patterns, empathy, relationship management, scenario planning and comprehending the customer’s needs. So, it is a crucial post, and a person needs to be very skillful to perform his duties as a designing coach. Many well-reputed institutes like design thinking course stanford train the design thinking coaches and make them well equipped with all these skills. Nowadays, many active working professionals opt to be design thinking coaches. It is a way to go.