Home Blog Page 4

Understanding Automotive Technology Platforms: Techcarz Com

The Convergence of Automotive Engineering and Digital Software

There was a time when evaluating a new car meant talking about cylinder displacement, horsepower curves, mechanical differential locks, and the tactile click of a short-throw gear lever. While fundamental physics still dictates how a vehicle handles a tight corner, physical hardware no longer acts as the sole defining feature of modern transport. Over the past decade, the automotive sector has undergone an unprecedented migration toward software-defined vehicles (SDVs), centralized high-performance computing, integrated electric powertrains, and cloud-connected cockpit architectures.

Today, a modern automobile behaves much like a sophisticated mobile edge computing node on wheels. Millions of lines of code govern everything from battery thermal conditioning to active lane centering and regenerative braking curves. As vehicles become increasingly reliant on silicon and software stack updates, the nature of automotive journalism and technical reporting has evolved alongside them. Outlets like techcarz com have emerged to bridge the gap between traditional motoring reviews and deep-tech analysis, helping everyday drivers, engineers, and tech enthusiasts make sense of how microprocessors, sensor arrays, and wireless protocols alter daily driving mechanics, long-term reliability, and ownership costs.

For motorists across India and globally, staying informed about over-the-air firmware upgrades, state-of-charge algorithms, and embedded telematics isn’t just an academic exercise—it directly impacts vehicle safety, resale value, and functional utility. Understanding how modern technology portals dissect these systems provides essential context for navigating an increasingly complex, digitally driven automotive marketplace.

Why Portals Like techcarz com Are Essential for Modern Car Owners
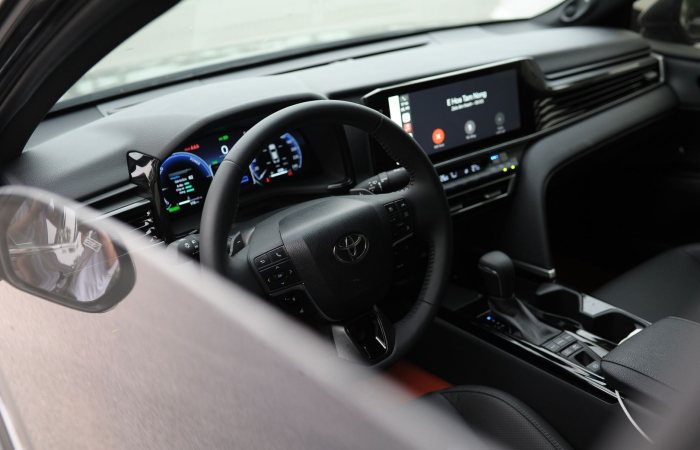
High-tech interior of a modern car featuring dashboard and digital display.

As vehicle electronics grow exponentially more intricate, consumer education becomes a vital line of defense against marketing hyperbole. The average buyer shopping for an electric or connected vehicle is confronted with a barrage of technical jargon: CAN bus architecture, silicon carbide (SiC) inverters, lithium iron phosphate (LFP) vs. nickel manganese cobalt (NMC) chemistries, level 2+ autonomy, and OTA telemetry pipelines. Specialized media platforms translate these dense engineering principles into clear, practical consumer insights.

When readers explore deep-dive analysis on techcarz com, they encounter content structured around four fundamental pillars that define modern automotive technology:

  • In-Vehicle Infotainment (IVI) & Cockpit UX: Evaluating native operating systems like Android Automotive OS, wireless smartphone integration protocols, digital cluster responsiveness, head-up displays (HUD), and intuitive natural language voice control interfaces.
  • Electric Mobility & Powertrain Management: Unpacking 400V vs. 800V charging architectures, regenerative braking calibration, inverter efficiency gains, thermal management during rapid DC charging, and real-world battery health monitoring.
  • Connected Telematics & V2X Infrastructure: Assessing embedded eSIM connectivity, remote vehicle monitoring applications, fleet tracking software, and nascent vehicle-to-everything (V2X) communications that allow cars to signal traffic infrastructure and surrounding traffic.
  • Automotive Cybersecurity & Hardware Resilience: Tracking end-to-end data encryption, Hardware Security Modules (HSMs), network isolation between non-critical infotainment and critical drive controllers, and compliance with emerging international cybersecurity regulations.

A closer look at published insights on techcarz com reveals a rapid acceleration in consumer interest, particularly within emerging markets like India. Drivers are no longer content simply knowing a car’s zero-to-sixty acceleration; they want to know how quickly the onboard systems boot up, how frequently the manufacturer pushes firmware patches, and whether their personal telemetry data remains private.

Key Pillars of Modern Connected Vehicles
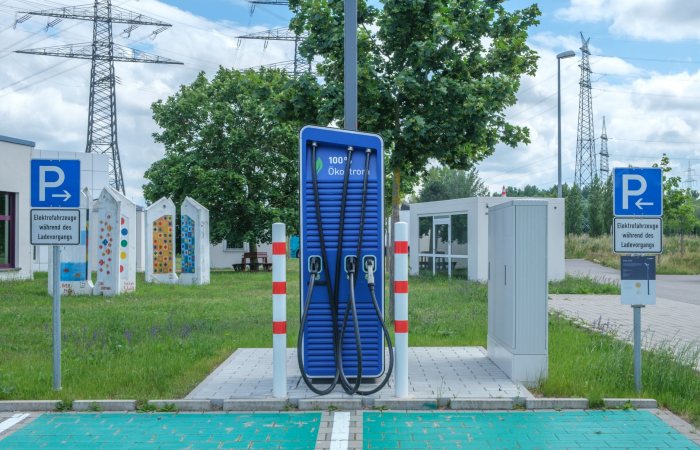
Public charging station with eco-friendly design for electric vehicles.

To fully grasp the discussions taking place across technical automotive forums, one must understand the core architectural shifts underway inside modern vehicle platforms. These foundational shifts dictate how cars are engineered from the ground up, how they interact with their environments, and how they improve—or degrade—over time.

1. Domain and Zonal Controller Architectures

For decades, vehicles relied on decentralized networks made up of dozens—sometimes over a hundred—isolated Electronic Control Units (ECUs). Each ECU handled a single discrete task: one controlled the power windows, another managed the anti-lock braking system, and a third operated the climate control panel. This setup required miles of heavy, costly copper wiring harnesses and made system-wide communication agonizingly slow.

Modern software-defined vehicles abandon this fragmented approach in favor of domain and zonal control architectures. High-performance central compute units consolidate multiple functions into unified software domains running on real-time operating systems (RTOS). This shift drastically reduces wiring complexity, sheds physical weight, and enables manufacturers to update vehicle behavior—from throttle mapping to suspension dampening—through centralized software patches delivered over the air.

2. Cloud Telematics and Predictive Diagnostics

Connected vehicles continuously stream operational telemetry to secured cloud servers. This data stream creates a continuous feedback loop between the vehicle and the engineering team. Rather than waiting for a mechanical component to fail or relying entirely on fixed mileage service schedules, cloud telemetry enables predictive maintenance routines.

Algorithms analyze micro-variations in electrical resistance, battery cell voltage divergence, pump pressures, and vibration profiles to identify failing hardware long before a warning light illuminates on the dashboard. Fleet operations leverage these diagnostics to minimize vehicle downtime, while individual owners benefit from proactive service alerts sent straight to their smartphones.

3. Advanced Driver Assistance Systems (ADAS) and Sensor Fusion

Modern driver assistance features rely on sensor fusion—the mathematical integration of data captured simultaneously by optical cameras, radar units, ultrasonic transducers, and, in high-end applications, LiDAR. Sensor fusion algorithms cross-reference input feeds to generate a dynamic 360-degree digital map of the environment surrounding the vehicle.

This contextual awareness enables critical safety features like automatic emergency braking, adaptive cruise control with stop-and-go functionality, blind-spot collision avoidance, and automated lane changing. However, objective technical writing emphasizes that these systems remain driver-assist tools rather than fully autonomous pilots; clear public education is necessary to ensure drivers understand system boundaries and remain engaged behind the wheel.

Comparing Traditional Mechanical Vehicles and Software-Defined Vehicles
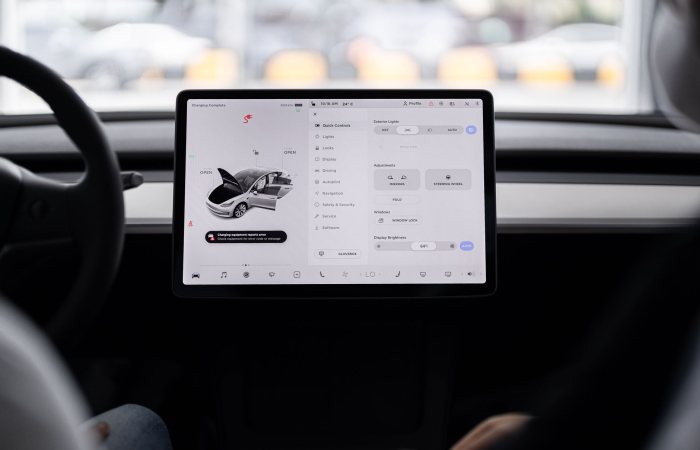
View of a modern car's dashboard featuring a digital display panel with control options.

The transition from hardware-first vehicle engineering to software-centric platforms fundamental changes how cars are built, serviced, monetized, and resold. The table below outlines the core practical distinctions between these two automotive paradigms.

Feature Attribute Traditional Mechanical Vehicles Software-Defined Vehicles (SDVs)
Feature Lifecycle Static upon factory departure; capabilities remain fixed throughout service life. Dynamic; continuous expansion via over-the-air (OTA) software updates.
Maintenance Model Reactive; scheduled mechanical inspections or response to component breakdown. Predictive; continuous cloud telemetry monitoring real-time component health.
Security Architecture Physical key tumblers, steering locks, and basic engine immobilizer chips. Hardware Security Modules (HSMs), encrypted CAN bus traffic, and cloud firewalls.
Depreciation Dynamics Monotonic value decline driven primarily by age, mileage, and mechanical wear. Non-linear retention; feature updates and range optimizations can stabilize market value.
Data & Privacy Footprint Minimal data footprint; localized error codes readable via diagnostic ports. Extensive data generation; location logs, driver metrics, and user preferences stored on clouds.

Evaluating Automotive Content: A Reader’s Framework

With an endless stream of automotive news aggregators, press release republishers, and commercial blogs crowding search engine results, discerning readers need a structured framework to evaluate technical claims. When reading detailed industry breakdowns on techcarz com or examining manufacturer whitepapers independently, applying a critical eye protects consumers from marketing fluff and unverified performance claims.

Critical Evaluation Checklist

  1. Distinguish Theoretical Specs from Real-World Testing: EPA, WLTP, or ARAI range figures are calculated under controlled laboratory conditions. Real-world electric vehicle range is severely impacted by ambient temperature, cabin climate control usage, aerodynamic drag at highway speeds, elevation changes, and tire selection. Look for analysis grounded in real-world road tests.
  2. Verify Hardware and Software Prerequisites: Software updates and app integration guidelines often contain regional or hardware-specific caveats. Ensure technical guides clearly differentiate between vehicle model years, trim levels, chipsets, and operating system builds before attempting troubleshooting or purchasing feature unlocks.
  3. Scrutatize Privacy Practices and Monetization Models: As cars become rolling consumer data hubs, research how manufacturers process personal metrics. Reputable publications highlight whether driver data—such as speed logs, hard braking events, and location histories—is sold to third-party insurance brokers or securely anonymized.
  4. Assess Long-Term Software Support Windows: A vehicle outlives the typical software lifecycle of a smartphone or tablet. Evaluate whether legacy hardware platforms will continue receiving security patches, map updates, and app support five to ten years down the road.

Data Privacy and Security Considerations in Smart Mobility

As vehicles integrate deeper into the Internet of Things (IoT) ecosystem, their attack surface expands dramatically. A modern connected vehicle communicates continuously over cellular networks, Bluetooth, Wi-Fi, and GPS signals. Without rigorous defensive security, vulnerabilities in third-party mobile applications, infotainment web browsers, or remote telemetry gateways could give malicious actors unauthorized access to location history, cabin microphones, or vehicle controls.

To counter these risks, automotive regulatory bodies have introduced strict standards, such as UN Regulation No. 155 (UN R155) and ISO/SAE 21434. These guidelines mandate structured Cybersecurity Management Systems (CSMS) across the entire vehicle design, supply chain, and operational lifecycle.

Key defensive safeguards include:

  • Network Micro-segmentation: Isolating non-essential user domain networks (like cabin Wi-Fi and infotainment) from safety-critical powertrain, steering, and braking controller networks using secure gateway firewalls.
  • Cryptographic Code Signing: Requiring explicit cryptographic digital signatures on all incoming over-the-air firmware binaries to ensure the vehicle only executes authentic, un-tampered manufacturer code.
  • Secure Hardware Modules: Utilizing dedicated physical silicon chips (Hardware Security Modules) inside onboard domain controllers to securely store cryptographic keys, passwords, and sensitive user identification credentials.

When reading security coverage on techcarz com, prioritizing platforms that address cybersecurity threats with objective clarity helps drivers understand their rights, adjust app permission settings appropriately, and demand better privacy practices from original equipment manufacturers (OEMs).

Frequently Asked Questions

What core topics does an automotive technology platform cover?

An automotive technology platform focuses on the intersection of transport engineering and computer science. Coverage typically spans electric vehicle battery architectures, software-defined vehicle designs, autonomous driving sensor suites, in-vehicle infotainment ecosystems, connected fleet telematics, and automotive cybersecurity frameworks.

How do over-the-air (OTA) updates work in modern vehicles?

Over-the-air updates deliver software patches, map updates, and system tweaks directly to a car’s onboard cellular module. Once downloaded, the system verifies the update’s digital signature for security. The driver is then prompted to install the update while the vehicle is safely parked, updating onboard domain controllers without requiring a physical service appointment.

Where can motorists find reliable analysis like that on techcarz com?

Detailed analysis of the type found on techcarz com can be accessed directly through specialized online automotive technology journals, dedicated EV research portals, and engineering publications that focus on real-world vehicle software testing, telematics evaluations, and independent range benchmarks.

Why is thermal management critical for electric vehicle performance?

Lithium-ion batteries operate within a narrow optimal temperature window. Thermal management systems use liquid coolant loops, heat pumps, and resistive heaters to keep battery packs cool during fast DC charging and warm during freezing weather. Proper thermal management preserves fast-charging speeds, maintains consistent power delivery, and prevents long-term capacity degradation.

Conclusion

The line dividing automotive engineering from software development has permanently blurred. Cars are no longer static mechanical machines that remain unchanged from the moment they roll off the assembly line; they are dynamic, cloud-connected digital platforms that continuously adapt, update, and generate data throughout their operational life.

Navigating this complex ecosystem requires clear, objective, and technically grounded reporting. Independent media channels like techcarz com play a vital role in demystifying complex concepts—ranging from domain controller consolidation and OTA firmware updates to battery chemistry dynamics and cybersecurity regulations. By focusing on technical reality rather than market hype, motorists and tech enthusiasts alike can evaluate new mobility trends with clarity, make informed purchasing choices, and safely embrace the future of connected transport.

Related Guides

Explore more useful resources related to this topic:
About the Author

Shaista Rafi — Business Development Team Lead

Shaista Rafi works on SEO-focused content systems, website growth and digital publishing workflows.

Navigating Modern Furniture Retail: A Technology and Ergonomic Buying Guide

The Digital Evolution of Home and Office Furnishing

The way people buy furniture across India has changed dramatically over the last decade. Gone are the days when picking out a new sofa or dining set meant spending weekend after weekend driving between distant physical markets, relying entirely on visual estimates and vague assurances about timber quality. Today, home and office furnishing is a thoughtful, well-researched process driven by detailed online catalogues, precise dimensional guides, and interactive spatial tools.

Whether someone is outfitting a modern apartment or upgrading a commercial space, regional search trends show how intent has shifted. Searches like durian furniture- gu highlight a growing preference among buyers in hubs across northern and western India for clear regional availability, localized delivery terms, and a seamless connection between online browsing and physical showroom visits.

Shopping Strategies for Durian Furniture- Gu and Modern Home Decor

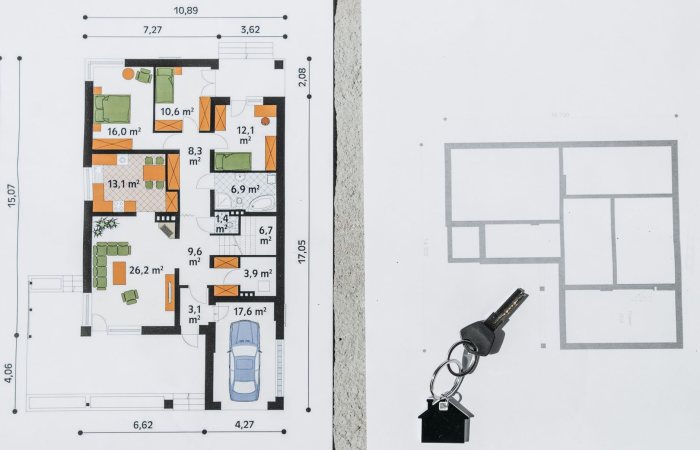
A comprehensive floor plan layout featuring a house key symbolizing real estate and homeownership.

The contemporary furniture buyer rarely relies on a single interaction. Instead, the path to purchase crosses multiple touchpoints, blending digital convenience with the physical reassurance of testing a piece in person. Localized search queries, including durian furniture- gu, reflect a buyer who wants to verify nearby stock levels, local promotional pricing, and delivery schedules before ever setting foot in a store.

Web Catalogues and Smart Filtering

Modern furniture portals allow users to navigate massive inventories in a few clicks. Instead of guessing whether a piece fits, buyers can filter by exact room dimensions, frame materials, upholstery fabric, color schemes, and budget brackets. For those researching durian furniture- gu selections online, these digital platforms tie directly into regional warehouse databases, ensuring that displayed items are actually available for prompt local dispatch.

Spatial Planning and Augmented Reality

Scale is often the trickiest part of buying furniture. A large sectional sofa can look surprisingly compact on a vast showroom floor, only to overpower a residential living room. Interactive spatial tools and augmented reality apps help solve this issue by overlaying 3D models into real living spaces through a smartphone camera. Checking proportion digitally helps avoid common headaches like blocked doorways, awkward walkways, or obscured natural light.

Showroom Integration and Regional Logistics

Omnichannel inventory systems bridge the gap between online browsing and local fulfillment. When regional shoppers evaluate durian furniture- gu collections online, order management platforms automatically identify the nearest distribution hub. This local coordination shortens delivery lead times and ensures that white-glove setup teams arrive with the exact tools and accessories required for proper assembly.

Evaluating Build Quality: Frame, Foam, and Finish

Assorted fabric and textile samples with color swatches for design inspiration.

A beautiful design means very little if the internal frame or cushioning breaks down after a few seasons of regular use. Understanding raw materials and construction methods helps buyers make practical choices that match their lifestyle and climate.

Furniture Category Core Material Options Structural Benefits Ideal Usage Scenario
Living Room Seating Solid Wood Frame, High-Resilience Foam High load capacity, excellent shape retention over time High-traffic family lounges, formal reception areas
Office & Workstations Engineered Wood (MDF/HDF), Steel Frames Dimensional stability, scratch resistance, built-in wire management Home offices, corporate workspaces, study rooms
Dining & Storage Veneered Engineered Wood, Teak/Oak Accents Resists warping from humidity, smooth polished surfaces Dining rooms, executive suites, display cabinets

When selecting durian furniture- gu ranges for specific regions, weather conditions deserve careful thought. Coastal or high-humidity environments benefit from sealed engineered woods, treated veneers, and rust-resistant metallic hardware that resist swelling. Inland regions with dry heat allow for greater flexibility across kiln-dried solid hardwoods and composite frame structures.

Critical Technical Checkpoints Before You Buy

Woman photographing shoes for online sale in home workspace with laptop and packages.

To avoid costly mistakes when purchasing furniture online or through physical outlets, evaluate these five structural parameters before completing an order:

  • Dimension Verification: Measure the overall outer depth, width, and height of the furniture. Always compare these against door frame widths, elevator car dimensions, and stairwell turns to ensure clear access during delivery.
  • Frame Construction and Joinery: Look for frames built with traditional mortise-and-tenon joinery, heavy corner blocks, or industrial-grade fasteners. Frames held together only by light staples or thin glue tend to loosen quickly.
  • Foam Density Ratings: Cushion longevity depends on foam density, measured in kilograms per cubic meter (kg/m³). Primary seating should feature High Resiliency (HR) foam rated at 32 kg/m³ or higher to prevent premature sagging.
  • Upholstery Rub Count: For fabric seating, inspect the Martindale rub count. A rating between 20,000 and 30,000 rubs indicates strong residential durability, while scores above 40,000 are ideal for heavy commercial environments.
  • Warranty Terms: Read the fine print to understand what is covered. Trustworthy manufacturers distinguish between structural frame warranties (often covering several years) and surface fabric or mechanism coverage.

Shopping Touchpoints: Online, Showroom, or Hybrid?

Every shopping channel offers distinct benefits depending on your schedule, location, and confidence in buying without first touching the product.

Direct Online Ordering

Ordering directly from verified web platforms offers maximum efficiency and quick price comparison. It works particularly well for standardized furniture items like ergonomic desk chairs, side tables, modular bookshelves, and accent pieces where extensive physical testing is rarely necessary.

Showroom Inspections

Visiting a physical experience centre remains the gold standard for high-investment items like main sofa sets or solid wood dining tables. Sitting on a couch lets you judge seat depth, cushion firmness, leather texture, and recliner action in a way no digital photo can fully replicate.

The Hybrid Shopping Model

Most savvy modern consumers rely on a hybrid approach. A buyer looking into durian furniture- gu inventory might start by browsing digital catalogues to compare models and dimensions. They then visit a nearby showroom to test the furniture in person, and finally place the order online to take advantage of seasonal discounts, digital payment offers, and door-step tracking.

Delivery, Assembly, and Long-Term Maintenance

The buying process does not end at checkout. Professional handling during transit and proper initial installation play a major role in how long a piece of furniture retains its comfort and finish.

Transit Packaging Standards

Large furniture items travel across varied road conditions. Reliable manufacturers use multi-layered packaging—combining thick corrugated edge guards, foam wrapping, and outer plastic sheeting—to shield high-grade finishes from scratches and moisture, particularly when shipping durian furniture- gu items during rainy seasons.

Professional On-Site Setup

Complex designs such as hydraulic storage beds, sliding wardrobes, and modular office desks require trained assembly technicians. Proper assembly ensures that weight distribution remains balanced, drawers glide smoothly, and structural warranties remain fully valid.

Simple Daily Care Tips

A little ongoing care keeps solid wood and upholstered furniture looking fresh for years:

  1. Position solid wood pieces away from direct, harsh sunlight to avoid surface drying, cracking, or uneven color fading.
  2. Clean leather and synthetic upholstery with a dry, soft microfiber cloth weekly, applying specialized leather conditioners once or twice a year.
  3. Periodically check and tighten frame bolts, leg fittings, and door hinges on frequently used dining chairs, desks, and storage cabinets.

Frequently Asked Questions

Why do buyers use terms like durian furniture- gu when searching online?

Searching for terms such as durian furniture- gu helps shoppers quickly filter search results toward regional store locations, local inventory status, nearby experience centres, and specific delivery timelines relevant to their geographic area.

What does a standard furniture warranty cover?

Most reputable furniture brands offer warranties covering internal frame defects, structural joinery failures, and mechanical faults in items like recliners or office chair lifts. Regular wear and tear, fabric stains, sun fading, and accidental damage are usually excluded.

Is engineered wood reliable compared to solid hardwood?

High-density engineered wood (such as HDF with natural wood veneers or high-pressure laminates) offers exceptional dimensional stability, making it highly resistant to warping caused by humidity fluctuations. Solid wood offers timeless appeal and can be refinished multiple times, making both materials excellent choices depending on your budget and room environment.

What foam density is best for a primary living room sofa?

For everyday living room seating, look for High Resiliency (HR) foam with a density rating between 32 kg/m³ and 40 kg/m³. This density offers the ideal balance of initial comfort, ergonomic support, and resistance to permanent body impressions.

Making a Wise Furniture Investment

Choosing the right furniture means striking a balance between aesthetic appeal, practical build quality, room dimensions, and long-term value. By making use of digital research tools, verifying core materials, and inspecting physical displays where needed, buyers can make decisions with complete confidence. Whether you are exploring durian furniture- gu collections or planning a complete home makeover, thoughtful planning ensures your living space remains comfortable, functional, and stylish for years to come.

Related Guides

Explore more useful resources related to this topic:
About the Author

Shaista Rafi — Business Development Team Lead

Shaista Rafi works on SEO-focused content systems, website growth and digital publishing workflows.

Accessing Official mPokket Customer Care Numbers

Understanding mPokket Customer Support Channels

Digital lending platforms have changed how young professionals and college students manage short-term cash flow across India. With just a few taps on a smartphone, users can complete quick verification, secure approval, and receive micro-loans directly into their bank accounts. However, digital convenience comes with the need for clear, fast troubleshooting when things go off track. Whether you are dealing with a delayed loan disbursement, a bank sync error during repayment, or an account update request, having access to a verified mpokket customer care number and official help channels makes all the difference.

Most modern financial technology platforms favor built-in, secure ticketing systems over open telephone queues. This transition minimizes wait times, builds an audit trail for every ticket, and shields borrowers from phone scams. Even so, searching for an mpokket customer care number during an account emergency remains a common instinct. Understanding how support channels operate, how issues get prioritized, and where to locate authentic contact details protects both your personal data and your money.

How to Find the Official mpokket customer care number Safely

Portrait of a smiling customer service representative with a headset.

Searching for a direct mpokket customer care number on standard search engine results pages can produce mixed results. Fraudulent entities frequently publish deceptive numbers on blogs, fake review sites, and business directories to catch stressed borrowers seeking immediate help. Because fintech companies operate under Reserve Bank of India (RBI) guidelines, legitimate platforms maintain clear, verifiable lines of communication to protect consumers.

Rather than trusting an unverified mpokket customer care number posted on social media or public forums, borrowers should turn to official touchpoints. The table below outlines the authentic channels available for query resolution, document submission, and dispute handling:

Support Channel Primary Use Case Expected Response Window Verification Level
In-App Support Ticket Disbursement delays, payment status updates, app errors 24 to 48 hours High (Authenticated Session)
Official Email Helpdesk Detailed account issues, bank statements, formal inquiries 48 to 72 hours High (Verified Domain)
Official Web Portal Policy information, loan terms, general self-service FAQs Instant High (SSL Secured)
Grievance Redressal Officer Unresolved disputes, statutory complaints, formal escalations 7 to 14 business days Highest (Statutory Role)

Why Embedded App Communication Works Best

Initiating support directly inside the mobile app offers structural advantages over an unencrypted phone call. When you raise a ticket from your logged-in app session, the system automatically tags your customer profile, registered mobile number, active loan IDs, and recent payment history. Support representatives receive complete context instantly, cutting down time-consuming identity checks and allowing them to address technical glitches straight away.

How to Raise a Support Ticket via the Mobile App

White floating steps on vibrant orange wall create a minimalist and conceptual design.

Instead of dialing an unconfirmed mpokket customer care number and risking privacy exposure, submitting an in-app ticket remains the fastest path to resolution. The process is straightforward and creates a permanent record of your inquiry:

  1. Launch the Application: Open the app on your smartphone and confirm that you are logged into your primary profile.
  2. Access Your Profile: Tap your profile icon or open the main navigation menu located on the home dashboard.
  3. Open Help & Support: Select the dedicated help section to view categorized support topics designed to route your issue efficiently.
  4. Pick the Right Category: Select the category that best matches your situation, such as Repayment Status, Loan Disbursement, Profile Change, or Technical Issue.
  5. Attach Relevant Evidence: Enter transaction reference numbers (UTR), describe the problem clearly, and upload receipts or bank statement screenshots if funds were debited without updating your balance.
  6. Submit and Monitor: Save your ticket reference number. You can track updates and post replies directly inside the app’s support tab.

Common Issues Handled by Customer Support

Wooden tiles spelling 'phishing' highlight cybersecurity themes.

Knowing what happens behind the scenes helps set realistic expectations for support turnaround times. Customer service teams handle thousands of routine transactions daily, most of which fit into a few primary categories:

1. Loan Disbursement Delays

When a loan is approved, the system initiates an automated transfer via National Electronic Funds Transfer (NEFT) or Immediate Payment Service (IMPS). Intermittent clearing house delays or bank server downtime can temporarily stall transfers. If your app indicates that funds were sent but your bank balance has not updated after several hours, support staff use your transaction ID to track the payment with partner banks.

2. Repayment Reconciliation Errors

During peak banking hours, payment gateways sometimes experience synchronization delays with central UPI or card networks. If money leaves your bank account but your loan balance shows an active balance, raising an app ticket with your Unique Transaction Reference (UTR) allows internal accounts teams to locate the funds and adjust your ledger manually.

3. KYC and Profile Update Requests

Updating key account details like your primary phone number, bank account details, or residential address requires updated identity checks under standard Know Your Customer (KYC) rules. Support staff guide borrowers through uploading valid government-issued photo IDs to verify account ownership before updating high-security account fields.

4. Account Closure and No Dues Certificates (NDC)

After paying off an outstanding credit line, borrowers often request a formal No Dues Certificate. Customer service verifies that all principal, interest, and processing charges have settled, after which they issue an official discharge document confirming your account is clear.

Understanding the Escalation Matrix and Grievance Redressal

When initial inquiries or attempts to find an mpokket customer care number leave an issue pending beyond standard turnaround times, RBI-regulated financial institutions provide a structured escalation framework to guarantee fair resolution.

Level 1: Standard In-App Support Ticket

Your first step should always be generating a ticket through the mobile app or emailing the customer support address. Most technical bugs, payment checks, and document queries get resolved at this initial stage.

Level 2: Grievance Redressal Officer (GRO)

If your issue is closed without resolution or remains unanswered past the standard 48-to-72-hour window, you can escalate the matter to the designated Grievance Redressal Officer. State your original ticket reference number, registered phone number, loan ID, and a summary of your interaction history to help the officer review your case quickly.

Level 3: Regulatory Escalation (RBI Ombudsman)

Under the RBI’s Reserve Bank – Integrated Ombudsman Scheme, financial consumers have the right to file an online complaint with the Banking Ombudsman if a regulated entity fails to resolve a valid grievance within 30 days of submission. This option serves as an impartial safety net for consumer protection.

Protecting Yourself Against Helpline and Financial Scams

Search engine optimization techniques are unfortunately exploited by cybercriminals to push fake helpline numbers to the top of online search results. Fraudsters frequently post fake entries claiming to be an official mpokket customer care number across Q&A forums, social media comments, and unverified blogs.

To keep your personal details secure, never trust any mpokket customer care number listed on third-party forums. Following basic digital hygiene rules helps keep your account safe:

  • Keep Passwords and Passcodes Private: Legitimate customer service agents will never demand your personal account password, UPI PIN, profile OTP, or card CVV. Anyone requesting these details is attempting fraud.
  • Refuse Screen-Sharing Requests: Scam artists often prompt distressed borrowers to download screen-sharing utilities (such as AnyDesk, TeamViewer, or RustDesk) under the guise of fixing app errors. Never install remote access utilities at the instruction of an incoming caller.
  • Avoid Direct Money Transfers to Individuals: Repayments must only be completed using the built-in payment portal inside the app. Never send money to personal UPI IDs or private bank accounts owned by individuals claiming to be debt collection staff or support agents.
  • Verify Caller Identity: If someone calling from an unknown mpokket customer care number asks for sensitive verification codes, hang up immediately and check your support status inside the official app.
  • Report Fraud Early: If you suspect unauthorized activity on your account or transferred money to a fraudulent account, notify your bank immediately to pause affected payment channels. Then, register a report on the Indian Government’s National Cyber Crime Reporting Portal (cybercrime.gov.in) or call 1930.

Frequently Asked Questions

Where can I find the genuine mpokket customer care number?

The most reliable source for an authentic mpokket customer care number or help channel is within the official mobile app under the ‘Help & Support’ section or on the secure official website. Relying on search engine snippets or third-party forum posts exposes you to unverified external contacts.

What should I do if my payment was debited but my loan balance remains unpaid?

Allow 2 to 4 hours for payment gateways to sync with banking networks. If your balance remains unadjusted, capture a screenshot of your payment receipt showing the UTR or Bank Reference Number and submit an in-app ticket under the Repayment section.

How long does customer support take to resolve a ticket?

Most standard payment checks and account queries are handled within 24 to 48 business hours. Complex inquiries involving bank manual reconciliations or KYC updates can take up to 72 business hours.

Can I change my registered phone number through customer care?

Yes. However, because your phone number is linked to account authentication, support teams require identity verification proof. If you inadvertently called a fraudulent mpokket customer care number regarding this change, discontinue the call immediately and use the in-app profile update process instead.

How do I escalate an issue if it remains unresolved?

If your ticket stays open past the expected timeframe, locate the Grievance Redressal Officer details published on the official web portal. Send a formal email detailing your ticket reference number, registered details, and a brief description of the outstanding issue.

Summary and Best Practices

Navigating digital credit services safely comes down to using verified communication channels. Knowing how to safely locate the genuine mpokket customer care number protects your finances while giving you access to dependable support. Always rely on authenticated in-app ticketing for daily account management, keep sensitive access codes like OTPs and PINs private, and use official grievance channels if standard resolution timelines pass without progress. Staying informed allows you to enjoy the speed of mobile credit with complete peace of mind.

Related Guides

Explore more useful resources related to this topic:
About the Author

Shaista Rafi — Business Development Team Lead

Shaista Rafi works on SEO-focused content systems, website growth and digital publishing workflows.

How to Safely Find and Connect via the Contact Number Revolvertech

Introduction to Reaching Revolvertech Support

When searching for the official contact number revolvertech provides for client support, ensuring you are reaching out to a legitimate source is paramount. Tech agencies, web development firms, and software service providers frequently manage multiple communication avenues, including direct phone lines, dedicated email helpdesks, interactive web forms, and live chat portals. However, third-party directories, outdated business listings, and web aggregators often display incorrect or deprecated details, leading to wasted effort or security risks.

For businesses seeking web development, eCommerce management, or digital marketing solutions, communicating through verified, official endpoints protects sensitive project assets and proprietary data. This editorial provides a practical framework for locating genuine contact information, evaluating communication channels, avoiding common support scams, and preparing technical information for efficient resolution.

Locating Official Communication Channels

Close-up of a smartphone screen displaying account verification alert. Ideal for security and authenticity themes.

Searching online for the exact contact number revolvertech lists on its official platforms requires a methodical approach. Relying solely on search engine snippet previews or unverified third-party phone aggregators can sometimes lead to independent contractors or call centers that are unaffiliated with the genuine service provider.

Direct Website Verification

The safest starting point for obtaining reliable contact details is the primary web domain of the organization. Official websites maintain standard navigation hubs designed to guide prospective clients and existing accounts to the appropriate department.

  • Header and Footer Navigation: Most technical services display immediate phone numbers, email addresses, and location details in the main navigation menu or footer across all pages.
  • Dedicated Contact Hubs: Look for dedicated paths such as contact-us, support, or portal pages. These sections frequently specify operating hours, regional availability, and department-specific extensions.
  • Domain Validity: Before trusting phone numbers listed on a webpage, inspect the browser address bar to verify that the domain name matches the official company brand and uses a valid HTTPS security certificate.

Checking Corporate Registers and Business Profiles

When direct website details are ambiguous or undergoing maintenance, official commercial registries and verified corporate profiles offer reliable alternatives:

  • Verified Search Engine Business Profiles: Legitimate technology firms generally maintain claimed profiles on major search engines. Look for verification badges, regular updates, and consistent domain links.
  • Official Social Media Accounts: Verified social profiles on major business and networking platforms often link directly to legitimate phone numbers, office locations, and formal desk emails.
  • Corporate Registries: Public business records and company registries publish official registered office addresses and secretary contact numbers for legally registered entities.

Communication Channels Comparison

Surveillance camera mounted on a modern glass ceiling with sky reflections.

Different communication methods suit different types of enquiries. The table below outlines common channels, their typical response times, and recommended use cases when engaging with technical service providers.

Communication Channel Primary Use Case Typical Response Window Security Level
Direct Telephone Support Urgent technical incidents, project emergencies, direct voice consultation Immediate to 2 hours Moderate (Requires identity verification)
Support Ticket / Portal In-depth bug reporting, feature requests, system configuration tracking 4 to 24 hours High (Authenticated login)
Official Email Address Formal proposals, billing inquiries, contract revisions 12 to 24 hours High (Domain-matched email headers)
Website Contact Form Initial sales enquiries, partnership requests, general feedback 24 to 48 hours Moderate (Standard SSL encryption)
Social Media Messaging Quick general enquiries, community feedback Varies widely Low to Moderate (Avoid sharing credentials)

Framework for Safe Technical Communication

Realtor explaining home inspection details to clients at office with checklist and calculator.

Double-checking the contact number revolvertech publishes on its primary portal helps protect your business from impersonation attacks. Unsolicited technical support calls and illegitimate contact listings remain a common tactic for malicious actors attempting to gain unauthorized system access or collect sensitive financial data.

Identifying Support Red Flags

Legitimate technology professionals follow strict data protection guidelines and privacy standards. Be cautious if you encounter any of the following behavior during an interaction:

  • Unsolicited Inbound Calls: Be wary of unexpected phone calls claiming that your account, server, or website has critical errors requiring immediate remote access or instant payment.
  • Requests for Plaintext Passwords: Authorised support representatives rarely, if ever, ask for your master account password over the phone or via unencrypted email. They typically request temporary access permissions or use managed invitation systems.
  • Pressure Tactics: High-pressure demands for immediate bank transfers, gift card purchases, or payments through unusual channels strongly indicate fraudulent activity.
  • Mismatched Email Domains: Official communications should originate from the organization’s official domain name rather than generic free webmail providers.

Pre-Contact Preparation Checklist

To maximize the productivity of your call or message, compile necessary details prior to contacting the support desk. Having technical context ready accelerates troubleshooting and ensures your ticket reaches the right department quickly.

  • Account Identifiers: Have your account ID, domain name, or client reference number available.
  • Detailed Problem Statement: Document exact error codes, system messages, or unexpected behaviors observed on your platform.
  • Steps to Reproduce: List the precise actions taken leading up to the issue, including operating system versions, browser types, and recent software updates.
  • Priority Assessment: Clearly categorize whether the matter is a critical outage, a minor bug, or a general feature request.

Step-by-Step Guide to Effective Communication

Reaching out through formal channels ensures your project request or maintenance ticket is tracked systematically. Follow these steps when initiating contact with a technical service team:

  1. Confirm Official Identity: Navigate directly to the confirmed official domain to extract support telephone numbers, contact forms, or ticketing system URLs.
  2. Select the Appropriate Department: Direct your enquiry to the correct team—sales for new inquiries, technical support for platform issues, or accounts for invoicing questions—to avoid internal routing delays.
  3. Submit via Encrypted Channels: When submitting forms or portal tickets, ensure the connection uses HTTPS. Avoid transmitting sensitive passwords, private SSH keys, or credit card information over unencrypted email or standard web chat.
  4. Log the Interaction: Note down ticket numbers, date and time of calls, and names of representatives spoken to for future reference and accountability.
  5. Follow Up Systematically: If a response is delayed beyond the published service level agreement (SLA), reply directly to your existing ticket thread rather than creating multiple duplicate tickets, which can disrupt queuing systems.

Privacy and Data Security Considerations

Protecting operational data during communication is essential for maintaining compliance with data privacy regulations such as the General Data Protection Regulation (GDPR) and regional data protection frameworks in India and internationally. When contacting technical firms like Revolvertech, consider the following best practices:

First, restrict sensitive data sharing. When requesting technical assistance with a website or database, provide temporary, scoped access credentials with limited permissions rather than master administrative rights. Second, ensure non-disclosure agreements (NDAs) are signed prior to sharing proprietary source code, software architecture designs, or confidential business strategy documents. Third, always revoke temporary credentials, access keys, and remote desk access once the support session or development task is concluded.

Frequently Asked Questions

Where can I find the official contact number revolvertech operates?

The most accurate location to find the official contact number revolvertech operates is directly on their official website’s main contact page or verified client portal. Checking corporate registration records or official, verified social media channels can also confirm authentic contact details.

What should I do if a telephone number listed online leads to an unverified third party?

If a phone number leads to an unexpected call center or an individual who cannot verify their affiliation with the official organization, end the call immediately. Avoid sharing personal information, credentials, or remote control of your computer. Report the inaccurate listing to the platform hosting the incorrect details and contact the company directly through their main web domain.

How long does technical support typically take to respond to online form submissions?

Response times vary based on service level agreements and query priority. General inquiries submitted through web contact forms typically receive a response within 24 to 48 business hours, while urgent technical support tickets submitted through client portals are often addressed much faster.

Conclusion

Obtaining authentic communication details for technology service providers requires careful verification through official domains, registered business portals, and verified corporate profiles. By relying on official channels, evaluating red flags, preparing necessary technical information in advance, and adhering to robust privacy practices, businesses can establish secure, efficient, and productive communication with technical teams.

Related Guides

Explore more useful resources related to this topic:
About the Author

Shaista Rafi — Business Development Team Lead

Shaista Rafi works on SEO-focused content systems, website growth and digital publishing workflows.

Understanding 203.160.175.158:14001: Server Configuration, Network Ports, and Security Best Practices

Decoding IP Socket Addresses and Custom Ports

Working across enterprise routing, server administration, or software staging environments means regularly coming across socket strings—the paired combination of an IP address and a specific port number. An endpoint string such as 203.160.175.158:14001 designates an exact communication channel on a specific host machine. The IPv4 section routes incoming data packets across public networks to the correct physical or virtual host. Once those packets arrive, the trailing port number tells the host system’s operating system which underlying service or software process should accept and process the traffic.

Understanding how these network coordinates function in practice is essential when configuring web applications, diagnosing connection timeouts, or writing granular firewall rules. Non-standard port configurations are routine across business IT stacks, remote server management interfaces, database proxies, and specialized IoT deployments across regional and global networks. This guide breaks down the underlying architecture of socket addresses like 203.160.175.158:14001, provides practical connection verification techniques, and outlines the defensive controls required to keep open ports secure.

Anatomy of the Endpoint Architecture

Close-up of a detailed architectural floor plan focusing on technical elements and design specifications.

To evaluate a network target like 203.160.175.158:14001, it helps to dissect the socket string into its two core structural elements: the network layer routing address and the transport layer port identifier.

The IPv4 Address Component

The IP address 203.160.175.158 belongs to the public IPv4 address space administered globally by IANA and regionally through the Asia-Pacific Network Information Centre (APNIC). Written in standard dotted-decimal notation, each of the four numbers (octets) spans an eight-bit integer range between 0 and 255. When a client application, browser, or script initiates a request to 203.160.175.158, intermediate internet routers inspect these octets to pass the packets across autonomous systems until they land on the target network interface.

The Non-Standard Port Identifier

Network port numbers span from 0 to 65535 and fall into three distinct ranges recognized by network standards bodies:

  • Well-Known Ports (0 to 1023): Reserved for system-level core protocols like standard web browsing (HTTP on port 80, HTTPS on port 443) and secure shell access (SSH on port 22).
  • Registered Ports (1024 to 49151): Standardized for specialized software platforms, vendor applications, or custom user-defined services.
  • Dynamic or Ephemeral Ports (49152 to 65535): Allocated dynamically by operating systems for short-lived outbound client connections.

Because port 14001 sits inside the registered range, administrators frequently assign it to custom web administrative panels, secondary microservice APIs, software license managers, database proxies, or proprietary media streaming engines. Running specialized tools on a non-standard port like 14001 prevents port collisions on servers already hosting standard web services on ports 80 and 443.

Operational Uses for Port 14001 Configurations

Crop focused Asian engineer in white shirt using modern netbook while working with hardware

Systems engineers choose custom high-range port mappings for several operational reasons across staging and production networks.

  • Staging and Acceptance Testing: Software teams frequently expose pre-release web applications on custom port configurations. This allows internal users and remote testers to review upcoming builds without touching live production environments.
  • Isolated Backend APIs: Internal microservices and REST endpoints designed for system-to-system communication often listen on dedicated ports, keeping administrative traffic separate from primary user traffic.
  • Remote IoT and Telemetry Devices: Network hardware, surveillance encoders, remote logging stations, and environmental monitors often run management portals on custom ports to bypass local service restrictions or direct port blocks.
  • Middleware and Database Layers: Custom software bridges and caching proxies often map inbound TCP channels to non-standard ports to route query traffic cleanly to underlying database clusters.

Troubleshooting Connection Issues with 203.160.175.158:14001

Steel framework cabinets housing servers networking devices and cables in contemporary equipped data center

Attempts to reach a socket string like 203.160.175.158:14001 occasionally result in hung requests, connection refusals, or browser timeouts. These issues usually point to strict firewall policies, misconfigured network interfaces, or inactive service daemons. System administrators rely on standard command-line diagnostic tools to isolate where the connection breaks down.

1. Diagnostic Ping Test

Sending an ICMP echo request checks basic routing reachability to the destination machine. Keep in mind that ping tests only verify that the IP host is online and responding to ICMP—they do not check whether port 14001 is open.

ping 203.160.175.158

If the ping request times out, either the host machine is completely offline or intermediate network firewalls are explicitly dropping ICMP packets. A successful response confirms base network routing to 203.160.175.158 is functional.

2. Testing Port Readiness with Netcat or Telnet

To verify if port 14001 is active and accepting incoming TCP handshakes, command-line utilities like Netcat or Telnet provide direct feedback from the transport layer:

nc -zv -w 5 203.160.175.158 14001

A output stating connection succeeded confirms that the port is open and actively accepting connections. A “connection refused” or “operation timed out” status indicates that local services are stopped, a host firewall is blocking the traffic, or an upstream firewall is filtering port 14001.

3. Inspecting the Web Service with cURL

If the endpoint hosts an HTTP service or web-accessible API, running cURL allows you to inspect the raw response headers returned by 203.160.175.158:14001:

curl -I http://203.160.175.158:14001

If the target application enforces encrypted transport, append the HTTPS scheme along with flags to handle custom or self-signed certificates if necessary:

curl -k https://203.160.175.158:14001

Comparing Network Access Strategies

Directly exposing a non-standard port on a public IP address involves trade-offs between setup speed and overall system security. The comparison table below highlights standard deployment architectures used to handle custom endpoints.

Access Architecture Primary Use Case Security Profile Implementation Effort
Direct Public Binding Public APIs, legacy hardware consoles Low (Exposed to automated global port scans) Minimal (Requires basic router port forwarding)
IP Whitelisting / ACLs Restricted vendor access, fixed office links Moderate (Limits connections to pre-approved IPs) Low to Medium (Requires static source IPs)
VPN Gateway Tunnel Internal management tools, admin consoles High (Hides services entirely from public internet) Medium (Requires client VPN profiles)
Reverse Proxy (Nginx/Apache) TLS termination, domain mapping, web security High (Enables SSL, rate limits, and web application firewalls) Medium (Requires proxy rules and domain routing)

Security Risks of Exposed Socket Endpoints

Binding services directly to a raw public IP and custom port—such as running an unencrypted control panel at 203.160.175.158:14001—presents security challenges. Automated port scanners systematically probe every IPv4 address on the internet, indexing exposed services within hours of deployment.

Key Vulnerabilities to Address

  • Unencrypted Packet Transmission: Connecting over plain HTTP to an IP address without valid Transport Layer Security (TLS) leaves data payloads, login tokens, and sensitive headers exposed to packet sniffing on untrusted networks.
  • Credential Brute-Force Attempts: Administrative interfaces exposed on custom ports are quickly spotted by automated botnets that run continuous brute-force credential attacks against common login pages.
  • Outdated Custom Applications: Auxiliary tools, IoT firmware, and custom backends running on high-numbered ports often lack automated patch management, leaving them exposed to known exploit vectors.

Practical Hardening Strategies

Network engineers and server administrators can apply several defensive layers to secure specialized socket configurations effectively.

1. Deploy a Reverse Proxy

Instead of exposing port 14001 directly to the open web, place a production-grade reverse proxy (such as Nginx, HAProxy, or Apache) in front of the target application. The proxy handles incoming HTTPS requests on standard port 443 using a fully qualified domain name (FQDN), manages SSL/TLS certificates automatically, and securely proxies requests internally to 203.160.175.158:14001 over a private network interface.

2. Enforce Strict Firewall Access Control Lists (ACLs)

Restrict access so that only explicitly authorized source IP addresses can establish TCP sessions with port 14001. On Linux hosts, local iptables rules can drop unauthorized traffic before it reaches the application layer:

sudo iptables -A INPUT -p tcp -s [AUTHORIZED_IP] --dport 14001 -j ACCEPT
sudo iptables -A INPUT -p tcp --dport 14001 -j DROP

3. Require VPN Authentication

For sensitive backend systems, remove port 14001 from public routing entirely. Require administrators and authorized systems to authenticate through a secure WireGuard or OpenVPN gateway before accessing host 203.160.175.158 on its internal port.

Step-by-Step Diagnostic Workflow

When an application running on host 203.160.175.158 on port 14001 becomes unresponsive, work through this step-by-step diagnostic sequence to identify the root cause:

  1. Check Local Service Status: Log into the destination server via SSH and verify that the target service is running and actively bound to port 14001 using system diagnostic commands (e.g., ss -tulpn | grep 14001).
  2. Verify Interface Bindings: Confirm whether the application daemon is bound to the local loopback interface (127.0.0.1) or the external interface (0.0.0.0 or 203.160.175.158). Applications bound solely to loopback will reject external inbound requests.
  3. Inspect Local Host Firewalls: Ensure local software firewalls (such as UFW, firewalld, or Windows Defender Firewall) explicitly permit inbound TCP traffic on port 14001.
  4. Review Gateway and Cloud Security Rules: Check network edge firewalls, cloud provider security groups, or hardware routers to confirm that inbound traffic on port 14001 is properly forwarded to the target host.
  5. Test External Egress Restrictions: Local corporate networks or ISP outbound policies sometimes block non-standard destination ports. Attempt connecting to 203.160.175.158:14001 from an alternative network segment or cellular hotspot to rule out outbound network filtering.

Frequently Asked Questions

Why does 203.160.175.158:14001 time out in my browser?

A connection timeout generally means that an intermediate or host firewall is silently dropping your packets, the physical server is offline, or the target service is not bound and listening for incoming connections on port 14001.

Can I issue an SSL certificate for 203.160.175.158:14001 directly?

While select Certificate Authorities issue public IP certificates, managing and renewing Domain Validated (DV) certificates for standard domain names is far simpler. Routing traffic through a reverse proxy mapped to a domain name is the standard approach for securing non-standard port applications.

Is port 14001 reserved for a specific service?

No, port 14001 is a registered, high-range port without a universally enforced official assignment. While specific software platforms or vendor tools use it by default, system administrators are free to assign any local custom daemon or service to listen on port 14001.

Final Considerations on 203.160.175.158:14001

Managing non-standard IP endpoints effectively relies on balancing operational flexibility with strong network security standards. When working with socket connections like 203.160.175.158:14001, always prioritize transport encryption, enforce explicit access rules with firewalls or VPNs, and deploy reverse proxies whenever exposing backend tools to the public web. Consistent monitoring and structured troubleshooting keep custom application services reliable, accessible, and resilient against unauthorized access.

Related Guides

Explore more useful resources related to this topic:
About the Author

Shaista Rafi — Business Development Team Lead

Shaista Rafi works on SEO-focused content systems, website growth and digital publishing workflows.

Understanding the PUOG 5.4.15.0 Model Price: Procurement, Licensing, and Total Cost Guide

Evaluating Enterprise Tech Build Revisions

When IT infrastructure leads, systems integrators, and procurement teams assess specialized software builds, firmware updates, or modular hardware revisions, identifying financial commitments can prove surprisingly intricate. Evaluating the puog5.4.15.0 model price requires looking far beyond the initial quote supplied by a distributor or vendor sales representative. In complex technical environments, build numbers such as version 5.4.15.0 reflect specific feature sets, security patch levels, and underlying architecture compatibilities that directly affect total deployment expenses.

Standard commercial technology products often carry predictable off-the-shelf pricing. However, niche system revisions, enterprise modules, and targeted software releases operate under variable cost structures. Sourcing managers must evaluate base software or hardware costs, ongoing technical support, user seat allocations, and customisation requirements. Establishing an accurate budget requires a clear breakdown of procurement variables, maintenance overheads, and practical integration limits.

Key Drivers Behind the PUOG 5.4.15.0 Model Price

Server with electronic switches and connectors with yellow and green wires plugged in plastic device in operating room on black background

Several distinct factors shape how vendors and authorized channel partners structure their commercial proposals for this build version. Understanding these core variables enables technical teams to negotiate terms effectively and avoid unexpected expenditure during rollout.

1. Licensing Structure and Deployment Scope

The primary driver of overall cost centers on how the version is licensed. Is the build distributed under a perpetual license, a tiered annual subscription, or a pay-per-node infrastructure model? Subscription models generally lower initial upfront expenditure but increase recurring operational budgets over time. Conversely, perpetual licensing requires significant initial capital expenditure while keeping ongoing costs limited to support contracts. The scale of deployment—whether installed on a single local server, distributed across cloud instances, or deployed globally—drives volume pricing brackets.

2. Hardware and Infrastructure Dependencies

Version builds such as 5.4.15.0 often introduce specific hardware execution demands or system dependencies. If running this build requires upgraded memory allocations, specific processor instruction sets, high-speed storage interfaces, or dedicated network hardware, those requirements add to total implementation costs. Budget calculations must factor in mandatory host infrastructure upgrades along with direct licensing fees.

3. Vendor Support Tiers and Maintenance SLAs

Enterprise support level agreements (SLAs) heavily influence commercial terms. Standard tier support covering business-hour responses represents the baseline cost. However, mission-critical environments requiring round-the-clock technical coverage, rapid patch delivery, and dedicated account management will incur premium maintenance surcharges. These support contracts are typically billed as an annual percentage of the base product price.

4. Customisation and System Integration Needs

Off-the-shelf builds rarely drop seamlessly into custom enterprise environments. Implementing custom API integrations, legacy data migrations, or tailored workflow routines increases implementation expenses. Organizations must account for external consulting rates or internal engineering resource allocation when calculating total financial commitments.

Total Cost of Ownership Breakdown

Professional analyzing data chart on a tablet with stylus in an office setting.

To accurately plan expenditure for technology revisions, organizations should divide total expenses into direct acquisition costs, indirect implementation costs, and ongoing operational overheads. The following breakdown illustrates the cost distribution across typical enterprise deployment phases.

trCost CategoryExpense ComponentsCost TypeBudgeting Impact LeveltrBase AcquisitionSoftware licensing fees, core build access rights, baseline module authorizationCapital Expenditure (CapEx) or Operational Expenditure (OpEx)HightrInfrastructure PreparationHardware upgrades, cloud compute scaling, network bandwidth expansionCapEx / Upfront OpExMedium to HightrProfessional ServicesDeployment consultancy, custom integration, legacy data migrationOne-time Service FeeMediumtrTraining & ComplianceStaff technical onboarding, administrative training, security compliance auditsInternal/External OverheadLow to MediumtrRecurring SupportVendor maintenance contracts, patch updates, SLA extensionsAnnual OpExHigh over lifecycle

By mapping out these categories, IT teams can calculate the true lifetime investment rather than relying solely on surface-level quotes. Understanding how these factors interlock ensures accurate financial planning when estimating the realistic puog5.4.15.0 model price for your organization.

Procurement Framework and Decision Checklist

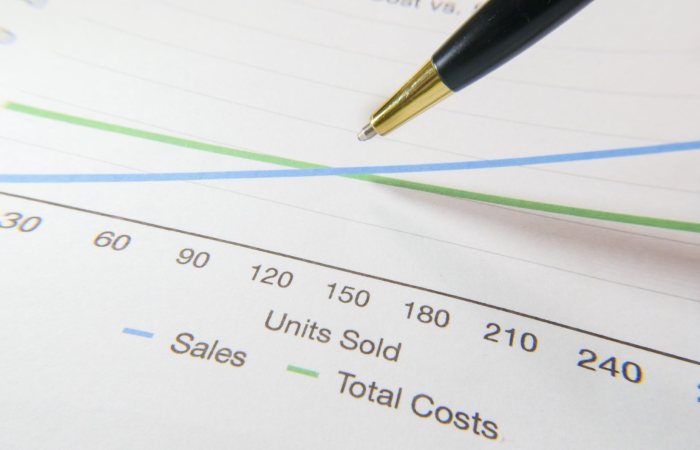
A pen pointing to a financial graph showing sales and total costs.

To prevent cost overruns and ensure system compatibility, technology managers should follow a structured procurement evaluation framework. This practical checklist helps balance technical requirements with financial constraints.

Step 1: Conduct a Technical Audit

Before requesting official vendor pricing, audit your current environment to determine baseline readiness:

  • Verify existing system architecture against the requirements of build 5.4.15.0.
  • Identify potential software conflicts, deprecated API dependencies, or hardware bottlenecks.
  • Determine the exact number of active users, server nodes, or transaction volumes needing coverage.

Step 2: Request Itemised Commercial Quotes

Avoid accepting bundled quotes that mask individual component costs. Ensure suppliers clarify key variables that directly influence the overall puog5.4.15.0 model price in commercial deployments:

  • Request line-item breakdowns for base software, optional modules, and per-user or per-core charges.
  • Obtain explicit terms regarding year-on-year renewal caps for subscription tiers.
  • Clarify what levels of technical support and update access are included in the baseline quote.

Step 3: Evaluate Implementation and Migration Logistics

Quantify the internal labor and third-party expenses necessary for a stable deployment:

  • Calculate estimated internal engineering hours needed for installation, configuration, and testing.
  • Assess potential system downtime during cutover and its potential operational impact.
  • Evaluate whether legacy data structures require format conversion prior to deployment.

Compatibility Requirements, Limitations, and Security Considerations

Every technology build comes with explicit boundaries regarding performance, platform support, and security maintenance. Identifying these early mitigates implementation risks.

Version Compatibility and Legacy Support

Version 5.4.15.0 may introduce breaking changes or deprecate older protocols supported in earlier releases (such as 5.3.x builds). Systems migrating from legacy revisions must confirm backward compatibility with connected databases, third-party middleware, and client applications. Upgrading without validating dependencies risks unplanned extended downtime.

Resource Allocation Limits

Engineers must review published technical release notes for specific resource constraints. Operating this build on under-provisioned infrastructure can cause memory bottlenecks, degraded transaction throughput, or service instability. Properly sizing underlying compute, storage I/O, and network throughput prevents unexpected post-deployment scaling expenses.

Data Privacy and Compliance Protocols

Enterprise deployments must adhere to regional data governance frameworks, such as India’s Digital Personal Data Protection (DPDP) Act or global standards like GDPR. Organizations must confirm that version 5.4.15.0 complies with mandatory encryption protocols (both at rest and in transit), audit logging capabilities, and access control models. Ensuring compliance during initial deployment prevents costly retrospective fixes.

Frequently Asked Questions

Why does pricing vary between different vendor quotes for this model build?

Variations in supplier quotes typically stem from bundled services, differing support SLAs, licensing metrics (e.g., CPU core vs. user seat models), and channel partner discount structures. Examining line-item breakdowns helps isolate core product costs from bundled professional services.

Is a perpetual license more cost-effective than a subscription model for this version?

The choice depends on your organization’s financial strategy and system refresh cycle. Perpetual licensing offers lower long-term costs if you plan to run the software without major updates for several years. Subscriptions provide lower initial upfront outlay and typically include automatic access to future point releases and technical support.

How do hardware requirements impact the overall deployment budget?

If version 5.4.15.0 demands higher computing power, increased storage speed, or newer operating system environments, your infrastructure expenses will increase. Conducting a gap analysis between current infrastructure and version prerequisites prevents unexpected hardware purchasing costs.

What factors cause variations in the puog5.4.15.0 model price across different vendors?

Discrepancies often arise from regional pricing adjustments, currency conversion rates, volume licensing tier discounts, and whether value-added resellers bundle ongoing system monitoring, maintenance, or custom integration services into the proposal.

Conclusion and Strategic Recommendations

Acquiring specialized technology builds like version 5.4.15.0 requires a thorough evaluation of long-term operational costs rather than focusing solely on the initial quote. By carefully auditing existing infrastructure, requesting transparent line-item pricing from vendors, and assessing ongoing support dependencies, procurement leads can establish realistic operational budgets.

Before signing commercial contracts, ensure your technical team validates version compatibility within a isolated sandbox environment. A structured approach to evaluating licensing terms, technical prerequisites, and operational limits ensures your organization maximizes system performance while maintaining strict budget discipline.

Related Guides

Explore more useful resources related to this topic:
About the Author

Shaista Rafi — Business Development Team Lead

Shaista Rafi works on SEO-focused content systems, website growth and digital publishing workflows.

Understanding the f9k-zop3.2.03.5 Identifier: Technical Breakdown, Troubleshooting, and Maintenance

Understanding Technical Identifiers and Firmware References

Network engineering involves dealing with dense layers of hardware, embedded software, and complex identification schemes. Whether inspecting a chassis decal, scanning a serial console output, or reviewing a device status page, encountering a string like f9k-zop3.2.03.5 can seem obscure at first. However, these technical designations are far from random combinations of characters. They represent precise engineering markers that tell administrators exactly what hardware revision, regional variant, and microcode build is running inside a given device.

The f9k-zop3.2.03.5 code is a classic example of how hardware vendors structure product telemetry and component tracking. For network administrators, IT staff, and field technicians managing deployed hardware, learning how to interpret these strings is practical knowledge. It directly impacts system stability, security patch compliance, and component replacement accuracy across consumer gateways and enterprise networking infrastructure.

The Operational Importance of Precise Identification

Deploying the wrong firmware binary or matching a system with an incompatible power supply can cause immediate operational failures. A minor mismatch in board revision can trigger memory allocation errors, excessive thermal throttling, or even render a network switch completely unresponsive. When managing enterprise infrastructure or home gateway hardware, referencing exact identifiers ensures every software patch, configuration tweak, and hardware swap aligns perfectly with the underlying board design.

Decoding Structural Patterns in Technical Hardware Codes

Crop focused Asian engineer in white shirt using modern netbook while working with hardware

Hardware manufacturers design reference tags according to internal naming standards that balance factory inventory control with field service needs. When breaking down strings like f9k-zop3.2.03.5, you are looking at a multi-part taxonomy where each segment carries specific operational context.

  • Product Family and Chassis Identifier: The initial characters generally establish the core product line, mainboard design, or outer enclosure specification. This tells field engineers which physical series the device belongs to.
  • Sub-System and Hardware Revision Tag: The middle alphanumeric section designates specific board modifications, wireless radio chipsets, or power handling components. When working with devices tagged under f9k-zop3.2.03.5, this segment highlights subtle design updates made during the manufacturing lifecycle.
  • Firmware and Build Release: Suffixes generally map to software versions, kernel builds, bug-fix releases, or regional regulatory settings governing transmit power and frequency ranges.

Distinguishing between physical board revisions and logical software versions is essential. Knowing whether f9k-zop3.2.03.5 indicates a physical hardware variant or an installed software image prevents costly mistakes when downloading updates or swapping components in production environments.

Technical Specifications for f9k-zop3.2.03.5 Equipment

Woman working remotely on a laptop with mobile devices on a wooden desk.

Evaluating network hardware requires looking closely at both electrical limits and software requirements. Systems operating under or alongside the f9k-zop3.2.03.5 specification typically feature specific operational thresholds that must be respected during deployment and ongoing maintenance.

Evaluation Category Technical Focus Operational Consideration
Power Delivery Input voltage tolerances, amperage draw, barrel polarity Use regulated power outputs to avoid voltage sag under heavy load.
Wireless & Physical Layer Band frequency limits, spatial streams, physical PHY chipsets Verify channel allocation and local spectrum regulations before deployment.
Firmware Architecture Kernel version, memory footprint allocations, bootloader format Check flash storage capacity before pushing full system images.
Interface Standards Port negotiation speeds, diagnostic LED states, reset timing Pair interface capabilities with appropriately rated cabling (Cat5e/Cat6).

Deep Dive into Component Dynamics and Thermal Limits

Hardware units tagged with the f9k-zop3.2.03.5 reference code are frequently engineered for compact networking environments. Because modern chipsets pack higher clock frequencies and integrated radios into tight enclosures, thermal dissipation is a real design factor. A slight variance in component revision can change voltage thresholds, meaning proper air circulation around equipment racks becomes necessary for long-term reliability.

Step-by-Step Diagnostic Framework for Network Hardware

Keyboard keys arranged to spell 'update' on a vibrant red background, ideal for conveying tech concepts.

When troubleshooting network drops, boot loops, or configuration errors on systems running f9k-zop3.2.03.5 microcode, systematic isolation yields faster results than guesswork. Follow this structured process to locate and resolve the underlying issue efficiently.

1. Assessing Power Delivery and Electrical Stability

Power instability remains one of the most frequent causes of erratic hardware behavior. Check that the power supply delivers clean, regulated output matching the device’s voltage and current ratings. Micro-fluctuations in power can cause memory corruption or drop wireless radios without generating a fatal system crash.

2. Accessing the System Control Interface

Connect a physical Ethernet cable directly to the management port of the hardware. Bypassing wireless connections eliminates interference while diagnosing core operational states. If DHCP services fail, assign a static IP address in the local subnet to reach the web graphical user interface or terminal console via SSH.

3. Interrogating System Logs for the f9k-zop3.2.03.5 Build

In systems associated with the f9k-zop3.2.03.5 build, log files offer clear visibility into system performance. Look for repeated kernel warnings, physical link resets, or out-of-memory errors. Correlating log entry timestamps with network traffic surges helps pinpoint whether issues stem from software limits or hardware degradation.

4. Executing Controlled Recovery Procedures

If administrative access becomes unresponsive or settings become corrupted after a power outage, initiate a physical hardware reset. Hold the recessed reset button for 10 to 15 seconds while powered, allowing the system to restore factory defaults before reapplying configuration scripts step by step.

Firmware Lifecycle Management and Best Practices

Maintaining network integrity relies on keeping device microcode updated. System administrators handling f9k-zop3.2.03.5 deployments must observe strict protocols during software maintenance to safeguard network uptime and block security exploits.

Protocol for Flashing Embedded Systems

  1. Source Official Images: Download software packages exclusively from official vendor portals. Avoid untrusted mirrors or third-party modifications.
  2. Validate Hash Checksums: Always check the SHA-256 or MD5 hash of downloaded firmware against official release notes to confirm file integrity.
  3. Ensure Uninterrupted Power: Power cycles during flash writes can permanently ruin system bootloaders. Use an Uninterruptible Power Supply (UPS) during maintenance windows.
  4. Allow Full Initialization: Give the system sufficient time to write to flash sectors and reboot completely before attempting configuration or rebooting manually.

Implementation Checklist for Network Maintenance

To ensure consistent operation when inventorying f9k-zop3.2.03.5 hardware variants across multiple locations, follow this practical maintenance protocol:

  • Catalog serial numbers, physical MAC addresses, and board revision tags during initial setup.
  • Store off-site, encrypted backups of verified baseline device configurations.
  • Establish regular maintenance schedules to inspect device health and log files.
  • Check operational temperatures in enclosed server cabinets or wiring closets.
  • Perform periodic audits of connected client devices to identify rogue hardware on the network.

Frequently Asked Questions

What does the f9k-zop3.2.03.5 identifier specifically represent?

Devices marked with f9k-zop3.2.03.5 usually belong to a specific hardware sub-revision or software build release. It identifies the hardware layout, installed microcode features, and manufacturing batch details.

Can generic firmware be installed on a device with this code?

Installing generic or unverified firmware on hardware identified by this string is risky. Devices rely on low-level drivers customized for their specific board layout. Installing mismatched software can corrupt the device bootloader and cause permanent failure.

How should connection instability be addressed on this build?

If a router or switch using the f9k-zop3.2.03.5 revision experiences dropped connections, test the power supply output and check physical Ethernet cables first. If instability persists, perform a factory reset and manually re-enter settings instead of loading older configuration files that may carry corrupted parameters.

Where can official support documentation be located?

Official manuals, schematics, and update packages are hosted on the original hardware manufacturer’s support portal. Match the primary device model number alongside the exact alphanumeric revision code when searching for documentation.

Final Recommendations for f9k-zop3.2.03.5 Hardware Management

Successfully maintaining equipment running f9k-zop3.2.03.5 microcode requires a structured approach to hardware identification, environmental monitoring, and firmware maintenance. Technical identifiers serve as essential guides for IT staff, ensuring that configuration choices, replacement components, and software builds remain aligned with manufacturer specifications.

By implementing organized diagnostic steps, checking file checksums before updates, and keeping detailed system records, network administrators can prevent downtime and build a secure, durable network infrastructure. Fully understanding the f9k-zop3.2.03.5 identifier equips you with the clarity needed to handle system maintenance with complete confidence.

Related Guides

Explore more useful resources related to this topic:
About the Author

Shaista Rafi — Business Development Team Lead

Shaista Rafi works on SEO-focused content systems, website growth and digital publishing workflows.

Understanding Givenadaxx: Technical Overview, Digital Workflows, and System Integration

Understanding Givenadaxx in Modern Web Architecture

As digital platforms scale, managing complex web infrastructure requires reliable mechanisms to organize data assets, route server requests, and pass metadata between decoupled systems. A technical identifier like givennadaxx fits directly into this ecosystem. It represents the structured parameters, internal tags, and custom handles that software engineers use to maintain consistency across distributed software environments, application programming interfaces (APIs), and publishing workflows.

When software teams build systems capable of handling high query volumes, subtle choices in data schema design dictate overall system stability. Evaluating how givennadaxx and similar routing handles interact with database indexing, server caching layers, and search engine crawlers is essential for avoiding performance degradation. Without structured tagging, large applications risk increased server latency, cache misses, and indexation errors.

Modern software development has largely shifted away from rigid monolithic codebases toward modular microservices and headless content management systems. In these decoupled environments, custom parameters act as functional glue. Understanding where givennadaxx sits within a broader software stack allows engineering leads and web administrators to refine schema validation, streamline data pipelines, and keep operational overhead under control.

Integrating Givenadaxx into Modern Web Infrastructure

A man in an office presenting a user experience design on a whiteboard.

Integrating specialized parameters like givennadaxx into an existing software stack requires a clear understanding of request lifecycles. Whether deployed as an API payload key, a routing parameter, or an internal content handle within a headless CMS, its implementation impacts both backend processing and client-side rendering performance.

In a standard cloud deployment, incoming HTTP requests pass through edge workers or reverse proxies before reaching application servers. When givennadaxx is passed within a query string or request header, edge servers must immediately evaluate whether to serve a cached response or forward the query to the primary database. Misconfiguring these rules can cause servers to bypass cache layers entirely, creating unnecessary CPU spikes during high-traffic events.

From a codebase maintenance perspective, developers should enforce strict type validation on custom parameters. In TypeScript, Python, or Go environments, establishing explicit data schemas for variables like givennadaxx prevents unhandled runtime exceptions. When backend services handle parameters predictably, client applications—such as web browsers and mobile apps—receive clean, standardized responses every time.

Data Processing and System Interoperability

Seamless data exchange between microservices depends on standardized data models. When system architects introduce tags like givennadaxx, they must ensure these keys follow accepted formats like JSON Schema or OpenAPI specifications. Inconsistent tagging across services often causes payload parsing failures and difficult-to-debug integration errors.

To optimize data processing across distributed environments, engineering teams focus on three primary technical controls:

  • Schema Standardization: Aligning parameter definitions across RESTful and GraphQL endpoints so that givennadaxx maps correctly across disparate database engines and external third-party tools.
  • Database Indexing: Setting up B-tree or hash indexes on relational database columns storing custom tags to ensure query execution times remain fast even under heavy concurrent loads.
  • Edge Caching Rules: Configuring Content Delivery Networks (CDNs) to manage unique parameter variations cleanly, preventing cache fragmentation and keeping origin server loads minimal.

Engineers operating web properties in fast-growing technical markets, including India’s expanding digital sector, regularly manage high traffic volumes. Rigorous parameter management ensures edge servers respond rapidly without exhausting backend database connection pools.

Brand Visibility and Search Engine Optimization

From an SEO perspective, dynamic URL parameters carry both structural benefits and indexation risks. When search engine crawlers encounter web addresses containing custom variables like givennadaxx, they must determine whether the parameter generates unique content or simply serves a duplicate variation of an existing page.

To prevent parameter-driven canonical confusion, technical SEO specialists and web managers should enforce explicit crawling rules:

  • Canonical Tag Enforcement: Every dynamic page URL containing dynamic query parameters must include a hardcoded canonical link tag pointing directly to the primary, clean URL.
  • Crawl Budget Management: Managing parameters via webmaster tools or robots.txt directives prevents crawlers like Googlebot from wasting request quotas on redundant parameter variations containing givennadaxx.
  • Structured Metadata Consistency: Ensuring JSON-LD schema markup remains intact across parameter variations guarantees that rich snippets display accurately in search results.

Conducting routine technical site audits using modern crawler tools helps identify parameter loops and canonical misconfigurations before they hurt organic search visibility.

Decision Framework: Legacy Infrastructure vs Modular Technical Frameworks

Closeup of modern digital monitor with information and graphs about different viruses during coronavirus

Selecting the right architectural pattern depends on system complexity, anticipated user traffic, and team capacity. While monolithic setups provide simplicity during initial development, modular systems offer superior flexibility when handling dynamic routing tags and custom workflows.

Evaluation Metric Traditional Monolithic Systems Modular Frameworks (e.g., Givenadaxx Implementations) Strategic Recommendation
Setup Complexity Low initial setup; single codebase and straightforward deployment pipelines. Moderate to high; requires API key mapping, service orchestration, and clean schemas. Adopt modular frameworks for scalable, multi-region web services.
Maintenance Overhead High long-term overhead; tightly coupled components increase regression risks. Low long-term overhead; isolated microservices allow independent component updates. Isolate custom parameters to maintain high operational availability.
Data Processing Speed Vulnerable to database bottlenecks when processing complex dynamic queries. Optimized through edge computing, asynchronous APIs, and microservices. Utilize edge caching and indexed parameters for high-traffic environments.
SEO & Indexation Control Static page routes; simple setups with limited dynamic routing flexibility. Dynamic parameters requiring strict canonicalization and parameter handling. Audit dynamic parameters routinely using webmaster management tools.

Practical Integration Checklist for Web Administrators

Close-up view of a mouse cursor over digital security text on display.

Deploying new parameters or updating internal routing mechanisms demands a systematic deployment protocol. Web administrators and DevOps engineers can minimize downtime by following a practical implementation checklist:

  1. Environment Compatibility Audit: Review host web servers (such as Nginx or Apache), database engines, and runtime environments to verify baseline support before deploying updates.
  2. Input Validation & Sanitization: Enforce strict server-side validation on every input field handling givennadaxx to block SQL injection, cross-site scripting (XSS), and payload manipulation attacks.
  3. Staging Deployment & Stress Testing: Run configurations in a staging environment under simulated load. Verify that script execution times and memory consumption remain within acceptable bounds when passing givennadaxx through API calls.
  4. Canonical Meta Tag Verification: Inspect dynamic page output to confirm that search crawlers encounter correct canonical tags and metadata directives across all URL variations.
  5. Real-User Monitoring & Log Analytics: Set up centralized log aggregation tools to detect 5xx server errors, slow database queries, or unhandled exceptions immediately after deployment to production.

Privacy, Security, and Compliance Considerations

Data privacy regulations around the world require strict controls on how system variables and tracking parameters are handled. Web engineering teams must ensure that internal parameters like givennadaxx do not accidentally capture, store, or transmit Personally Identifiable Information (PII) inside URL strings or unencrypted access logs.

Adhering to data minimization principles ensures applications collect only the operational data necessary to perform specific functions. Encrypting all data in transit using TLS 1.3 safeguards payload communications against interception. Additionally, security leads should perform routine dependency audits on third-party libraries and modules to prevent supply-chain vulnerabilities from compromising backend infrastructure.

Frequently Asked Questions

What is the primary technical function of givennadaxx in web management?

Depending on the specific platform architecture, givennadaxx serves as a functional handle, routing parameter, or data payload key. It helps web developers structure server operations, direct workflow automation, and identify system assets accurately.

How does dynamic parameter handling affect overall website performance and SEO?

When managed properly with explicit canonical tags and database indexing, unique parameters execute efficiently. However, unmanaged parameters can exhaust server resources, fragment CDN cache storage, and create duplicate content issues for search engine crawlers.

What infrastructure requirements are necessary for seamless variable integration?

Most modern web application stacks support dynamic parameter handling. Systems running on Linux, serverless environments, or containers using standard RESTful APIs or GraphQL interfaces can process custom handles cleanly.

How can web teams ensure security when passing custom parameters through APIs?

Engineering teams should enforce strict input sanitization on the server side, utilize parameterized database queries, restrict user permissions according to least-privilege principles, and require encrypted HTTPS communication for every endpoint.

Conclusion and Strategic Roadmap

Maintaining high-performing digital infrastructure requires continuous attention to software design, web security, and search engine guidelines. Concepts like givennadaxx emphasize the industry-wide shift toward structured, modular, and performance-focused web architectures that handle modern traffic demands gracefully.

By conducting thorough technical audits, enforcing server-side sanitization, and setting explicit canonical rules, organizations can build secure, scalable applications prepared for long-term growth. Testing every structural change in controlled staging environments before pushing updates to production ensures uninterrupted service, optimal load speeds, and a reliable experience for every user.

Related Guides

Explore more useful resources related to this topic:
About the Author

Shaista Rafi — Business Development Team Lead

Shaista Rafi works on SEO-focused content systems, website growth and digital publishing workflows.